首页 文章 精选 留言 我的

精选列表

搜索[剪贴板管理],共10005篇文章
优秀的个人博客,低调大师

openstack 命令行管理十一 - 安全组管理 (备忘)

 参考官方资料 You must modify the rules for the default security group because users cannot access instances that use the default group from any IP address outside the cloud. You can modify the rules in a security group to allow access to instances through different ports and protocols. For example, you can modify rules to allow access to instances through SSH, to ping them, or to allow UDP traffic – for example, for a DNS server running on an instance. You specify the following parameters for rules: Source of traffic. Enable traffic to instances from either IP addresses inside the cloud from other group members or from all IP addresses. Protocol. Choose TCP for SSH, ICMP for pings, or UDP. Destination port on virtual machine. Defines a port range. To open a single port only, enter the same value twice. ICMP does not support ports: Enter values to define the codes and types of ICMP traffic to be allowed. Rules are automatically enforced as soon as you create or modify them. 注: 已通过测试, 修改默认 secgroup 或自定义 secgroup 都可以完成数据访问测试 帮助 [root@station140 ~(keystone_admin)]# nova help | grep secgroup add-secgroup Add a Security Group to a server. list-secgroup List Security Group(s) of a server. remove-secgroup Remove a Security Group from a server. secgroup-add-group-rule secgroup-add-rule Add a rule to a security group. secgroup-create Create a security group. secgroup-delete Delete a security group. secgroup-delete-group-rule secgroup-delete-rule secgroup-list List security groups for the current tenant. secgroup-list-rules secgroup-update Update a security group. 创建自定义安全组 [root@station140 ~(keystone_admin)]# nova secgroup-create terry "allow ping and ssh" +--------------------------------------+-------+--------------------+ | Id | Name | Description | +--------------------------------------+-------+--------------------+ | 6966a8e4-0980-40ad-a409-baac65b60287 | terry | allow ping and ssh | +--------------------------------------+-------+--------------------+ 列出当前所有安全组 [root@station140 ~(keystone_admin)]# nova secgroup-list +--------------------------------------+---------+--------------------+ | Id | Name | Description | +--------------------------------------+---------+--------------------+ | 91a191a6-b89e-4f87-99c0-0fb985985978 | default | default | | 6966a8e4-0980-40ad-a409-baac65b60287 | terry | allow ping and ssh | +--------------------------------------+---------+--------------------+ 列出某个组中的安全规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+----------+--------------+ | | | | | default | | | | | | default | +-------------+-----------+---------+----------+--------------+ 增加规则方法 (允许 ping) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry icmp -1 -1 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 增加规则方法 (允许 ssh) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry tcp 22 22 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 增加规则方法 (允许 dns 外部访问) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry udp 53 53 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 列出自定义组规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules terry +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | | udp | 53 | 53 | 0.0.0.0/0 | | | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 尝试修改 default secgroup 列出 default secgroup 规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+----------+--------------+ | | | | | default | | | | | | default | +-------------+-----------+---------+----------+--------------+ 添加规则 (允许 ping) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default icmp -1 -1 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 添加规则 (允许 ssh) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default tcp 22 22 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 添加规则 (允许 dns外部访问) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default udp 53 53 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 列出默认组规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | | | | | default | | icmp | -1 | -1 | 0.0.0.0/0 | | | tcp | 22 | 22 | 0.0.0.0/0 | | | | | | | default | | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 删除某个实例, 使用中的规则 nova remove-secgroup terry_instance1 terry 注: 在虚拟机启动后, 无法在增加其他规则 

优秀的个人博客,低调大师

openstack 命令行管理十五 - 浮动 IP 管理 (备忘)

帮助 [root@station140 ~(keystone_admin)]# nova help | grep float add-floating-ip Add a floating IP address to a server. floating-ip-bulk-create Bulk create floating ips by range. floating-ip-bulk-delete Bulk delete floating ips by range. floating-ip-bulk-list List all floating ips. floating-ip-create Allocate a floating IP for the current tenant. floating-ip-delete De-allocate a floating IP. floating-ip-list List floating ips for this tenant. floating-ip-pool-list List all floating ip pools. remove-floating-ip Remove a floating IP address from a server. 生成 浮动 IP [root@station140 ~(keystone_admin)]# nova floating-ip-create pub1 +----------------+-------------+----------+------+ | Ip | Instance Id | Fixed Ip | Pool | +----------------+-------------+----------+------+ | 192.168.48.143 | None | None | pub1 | +----------------+-------------+----------+------+ 分配 [root@station140 ~(network_admin)]# nova add-floating-ip terry_instance1 192.168.48.143 查询浮动 IP 分配情况 [root@station140 ~(keystone_admin)]# nova floating-ip-list +----------------+--------------------------------------+-----------+------+ | Ip | Instance Id | Fixed Ip | Pool | +----------------+--------------------------------------+-----------+------+ | 192.168.48.143 | 93d0c9c1-b38b-4fe3-9ae3-400f43276f60 | 10.0.0.50 | pub1 | +----------------+--------------------------------------+-----------+------+ 移除浮动 IP [root@station140 ~(keystone_admin)]# nova floating-ip-delete 192.168.48.143 

优秀的个人博客,低调大师

数据源管理 | 分布式NoSQL系统,Cassandra集群管理

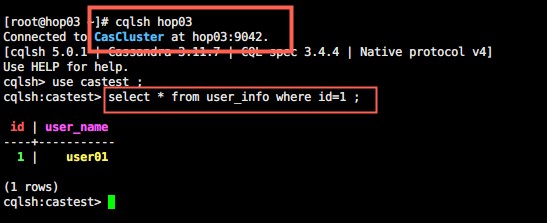
本文源码:GitHub·点这里 || GitEE·点这里 一、Cassandra简介 1、基础描述 Cassandra是一套开源分布式NoSQL数据库系统。它最初由Facebook开发,用于储存收件箱等简单格式数据,此后,由于Cassandra良好的可扩展性,逐渐发展成为了一种流行的分布式结构化数据存储方案。 2、特点分析 弹性可扩展性 Cassandra是高度可扩展的;它允许添加更多的硬件以适应更多的客户和更多的数据根据要求,可以根据业务的数据流量轻松扩展集群规模。 架构特点 Cassandra可以基于分布式运行,并采用了许多容错机制。由于去中心化无主的策略,所以没有单点故障。可以做到不停服滚动升级。这是因为Cassandra可以支持多个节点的临时失效(取决于群集大小),对群集的整体性能影响可以忽略不计。并且Cassandra提供多地域容灾。Cassandra允许将数据复制到其他数据中心,并在多个地域保留多副本,十分适用于不能承担故障的关键业务,必须持续提供服务的应用程序。 数据存储机制 Cassandra适应所有可能的数据格式,包括:结构化,半结构化和非结构化。可以根据业务的需要动态地适应变化的数据结构,并且通过在多个数据中心之间复制数据,可以灵活地在需要时分发数据。有许多案例证明Cassandra可以在金融,医疗,物联网等领域使用。 资源整合能力 Cassandra可以很容易的跟其他开源组件做集成,其中包括Hadoop,Spark,Kafka,Solr等系列组件,成为大数据业务处理里面重要的一个角色。 二、集群环境搭建 1、环境概览 jdk1.8 apache-cassandra-3.11.7-bin.tar.gz centos7 三台服务:hop01、hop02、hop03节点 2、安装包处理 tar -zxvf apache-cassandra-3.11.7-bin.tar.gz mv apache-cassandra-3.11.7 cassandra3.11 3、环境变量 [root@hop01 opt]# vim /etc/profile export CASSANDRA_HOME=/opt/cassandra3.11 export PATH=$PATH:$CASSANDRA_HOME/bin [root@hop01 opt]# source /etc/profile 4、创建目录 # 数据目录 mkdir -p /data/cassandra/data # 日志目录 mkdir -p /data/cassandra/log 5、集群配置 vim /opt/cassandra3.11/conf/cassandra.yaml # 配置集群名称 cluster_name: 'CasCluster' # 配置数据目录 data_file_directories: - /data/cassandra/data # 配置日志目录 commitlog_directory: /data/cassandra/log # 设置监听地址,当前服务IP listen_address: 192.168.72.132 # 配置RPC服务 start_rpc: true rpc_address: 192.168.72.132 # 配置集群节点 seed_provider: - class_name: org.apache.cassandra.locator.SimpleSeedProvider parameters: - seeds: "192.168.72.132,192.168.72.138,192.168.72.139" 将该配置分发到集群的每个节点,注意listen_address和rpc_address是节点自己的IP地址即可。 6、启动集群 # 集群下节点依次执行启动命令 cassandra -R # 查看节点状态 nodetool status 7、基础操作 进入命令行 cqlsh hop01 创建keyspace,并选择 CREATE KEYSPACE IF NOT EXISTS castest WITH REPLICATION = {'class': 'SimpleStrategy','replication_factor':3}; use castest ; 创建表,写入数据 CREATE TABLE user_info (id int, user_name varchar, PRIMARY KEY (id) ); INSERT INTO user_info (id,user_name) VALUES (1,'user01'); 查询数据 select * from user_info ; 基于其他服务查看数据,可以看到数据已经在集群间做了同步过程: 三、集成SpringBoot框架 1、核心依赖 <dependency> <groupId>org.springframework.boot</groupId> <artifactId>spring-boot-starter-web</artifactId> <version>${spring.boot.version}</version> </dependency> <dependency> <groupId>org.springframework.boot</groupId> <artifactId>spring-boot-starter-data-cassandra</artifactId> <version>${spring.boot.version}</version> </dependency> <dependency> <groupId>org.springframework.boot</groupId> <artifactId>spring-boot-starter-data-jpa</artifactId> <version>${spring.boot.version}</version> </dependency> 这里核心需要cassandra依赖和操作的API依赖。 2、核心配置 spring: data: cassandra: keyspace-name: castest contact-points: 192.168.72.138,192.168.72.132,192.168.72.139 port: 9042 cluster-name: CasCluster keyspace-name:类似关系型数据库的名称; contact-points:集群下节点的IP地址; port:默认端口; cluster-name:上述配置的集群名称; 3、基于Template命令 CassandraTemplate模板类,实现了一系列操作Cassandra数据库的基本方法,直接注入即可使用。 @Repository public class UserInfoTemplate { @Resource private CassandraTemplate cassandraTemplate ; // 查询全部数据 public List<UserInfo> getList (){ return cassandraTemplate.select("SELECT * FROM user_info",UserInfo.class) ; } // 添加数据 public UserInfo insert (UserInfo userInfo){ return cassandraTemplate.insert(userInfo) ; } // 根据主键查询 public UserInfo selectOneById (Integer id){ return cassandraTemplate.selectOneById(id,UserInfo.class) ; } // 修改数据 public UserInfo update (UserInfo userInfo){ return cassandraTemplate.update(userInfo) ; } // 删除数据 public Boolean deleteById (Integer id){ return cassandraTemplate.deleteById(id,UserInfo.class) ; } } 4、基于Repository接口 SpringBoot框架中定义的数据库访问核心接口。 接口实现 import com.cassand.cluster.entity.UserInfo; import org.springframework.data.repository.CrudRepository; public interface UserInfoRepository extends CrudRepository<UserInfo,Integer> { } 接口用法 @Service public class RepositoryService { @Resource private UserInfoRepository userInfoRepository ; // 保存 public UserInfo save (UserInfo userInfo){ return userInfoRepository.save(userInfo) ; } // 查询 public UserInfo getById (Integer id){ return userInfoRepository.findById(id).get() ; } // 修改 public UserInfo update (UserInfo userInfo){ // 主键ID存在的情况即为修改 return userInfoRepository.save(userInfo); } // 删除 public void deleteById (Integer id){ userInfoRepository.deleteById(id); } } 5、实体表结构 注意这里的注解是基于cassandra特定的一套。 import org.springframework.data.cassandra.core.mapping.Column; import org.springframework.data.cassandra.core.mapping.PrimaryKey; import org.springframework.data.cassandra.core.mapping.Table; @Table("user_info") public class UserInfo { public UserInfo(Integer id, String userName) { this.id = id; this.userName = userName; } @PrimaryKey private Integer id ; @Column(value = "user_name") private String userName ; } 四、源代码地址 GitHub·地址 https://github.com/cicadasmile/data-manage-parent GitEE·地址 https://gitee.com/cicadasmile/data-manage-parent


资源下载

更多资源
Mario

Mario

马里奥是站在游戏界顶峰的超人气多面角色。马里奥靠吃蘑菇成长,特征是大鼻子、头戴帽子、身穿背带裤,还留着胡子。与他的双胞胎兄弟路易基一起,长年担任任天堂的招牌角色。

腾讯云软件源

腾讯云软件源

为解决软件依赖安装时官方源访问速度慢的问题,腾讯云为一些软件搭建了缓存服务。您可以通过使用腾讯云软件源站来提升依赖包的安装速度。为了方便用户自由搭建服务架构,目前腾讯云软件源站支持公网访问和内网访问。

Nacos

Nacos

Nacos /nɑ:kəʊs/ 是 Dynamic Naming and Configuration Service 的首字母简称,一个易于构建 AI Agent 应用的动态服务发现、配置管理和AI智能体管理平台。Nacos 致力于帮助您发现、配置和管理微服务及AI智能体应用。Nacos 提供了一组简单易用的特性集,帮助您快速实现动态服务发现、服务配置、服务元数据、流量管理。Nacos 帮助您更敏捷和容易地构建、交付和管理微服务平台。

WebStorm

WebStorm

WebStorm 是jetbrains公司旗下一款JavaScript 开发工具。目前已经被广大中国JS开发者誉为“Web前端开发神器”、“最强大的HTML5编辑器”、“最智能的JavaScript IDE”等。与IntelliJ IDEA同源,继承了IntelliJ IDEA强大的JS部分的功能。

用户登录
用户注册