首页 文章 精选 留言 我的

精选列表

搜索[子系统命令],共10000篇文章
优秀的个人博客,低调大师

一个cp命令引发的mongodb大量慢查询

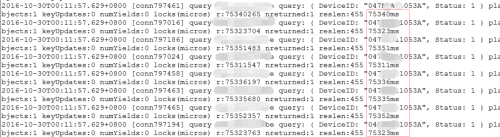
遇到问题:凌晨收到报警,某mongodb服务器cpu load超过8。由于没有影响到业务,第二天一早开始查原因。 查原因: 1. 先了解该服务器上的应用有哪些 该db服务器主要应用只有mongodb。于是开始查询mongodb日志: 通过凌晨的日志mongodb.log查看,有大量的慢查询,但实际上这些表都非常小,只有几百行数据,而且表还有索引,却仅仅一个查询花了60~80s,慢查询之后的日志显示该节点不被其他节点检测到(mongodb复制集形式)。 由于一个小表的查询都需要判断70s左右,而且mongodb部署的是复制集形式(其他的查询节点都是正常的)可以判断,可能是这台db的性能方面影响了mongodb,而非mongodb本身的性能影响。 2. 于是查看凌晨有什么任务再跑。 crontab -l 发现确实凌晨有一个任务。是一个切割日志的脚本。大概就是把日志cp到另一个目录,然后将当前日志清空,继续记录新的一天的日志。 但这个日志平时都较小,也运行了很长时间.只能试一试的看看日志目录 看到日志突然就这么大了。难道是因为晚上cp 文件的时候导致了? 差不多判断问题出现在 cp导致了io负载过高,进而导致了cpu load 过高。 3. 复现问题 由于该操作在夜间操作,未影响线上业务。故手动操作cp,复现问题。 cp 了一个近3g的文件, 如下图:看到产生的I/O请求太多,I/O系统已经满负荷,该磁盘可能存在瓶颈。 跟着cpu load也 上升到10 (每一分钟的cpu load 值)左右。 解决问题: 将较大的日志从mongodb服务器分离出。 将小日子日志脚本切割改为系统logrotate切割。logrotate会在系统空闲的状态进行操作。 可是为什么拷贝了一个3g的文件,就会导致cpu load 高达10. 进而导致mongodb查询性能直线下降。 于是我们联系了某云,一个普通云盘的性能怎会如此低! 以上查问题的思路,最开始也没有很顺利。起初文件较小并没有猜测到是日志拷贝。查问题的时候不能以惯性思维排除。

优秀的个人博客,低调大师

openstack 命令行管理五 - 磁盘配额管理(备忘)

 磁盘配额由 Swift 1.8 (OpenStack Grizzly) 管理 Container Quotas: Limits the total size (in bytes) or number of objects that can be stored in a single container. Account Quotas: Limits the total size (in bytes) that a user has available in the Object Storage service. [root@station140 ~(keystone_admin)]# cinder help | grep quota quota-class-show List the quotas for a quota class. quota-class-update Update the quotas for a quota class. quota-defaults List the default quotas for a tenant. quota-show List the quotas for a tenant. quota-update Update the quotas for a tenant. quota-usage List the quota usage for a tenant. 配额默认针对 tenants 级别, 倒不如改成针对用户级别更方便管理 下面方法限制用户在所有 project 中的磁盘总大小 /etc/glance/glance-api.conf user_storage_quota = 0 <- 以 byte 进行计算 ex: 5368709120 (5G) ex: icehouse 版本后, 需要修改配置文件 glance-api.conf 中 image_member_quota 配置 默认配额配置文件 /etc/cinder/cinder.conf #quota_volumes=10 #quota_snapshots=10 #quota_gigabytes=1000 分别查询, 默认或某个 project 配额 [root@station140 ~(keystone_admin)]# cinder quota-defaults default +-----------+-------+ | Property | Value | +-----------+-------+ | gigabytes | 1000 | | snapshots | 10 | | volumes | 10 | +-----------+-------+ [root@station140 ~(keystone_admin)]# cinder quota-show 9467f30b8bba4770a06a687e4584636b <- 可选 cloud +-----------+-------+ | Property | Value | +-----------+-------+ | gigabytes | 1000 | | snapshots | 10 | | volumes | 10 | +-----------+-------+ 修改 cloud 配额 [root@station140 ~(keystone_admin)]# cinder quota-update --volumes 15 cloud 查询修改后设定 [root@station140 ~(keystone_admin)]# cinder quota-show cloud +-----------+-------+ | Property | Value | +-----------+-------+ | gigabytes | 1000 | | snapshots | 10 | | volumes | 15 | +-----------+-------+

优秀的个人博客,低调大师

openstack 命令行管理十一 - 安全组管理 (备忘)

 参考官方资料 You must modify the rules for the default security group because users cannot access instances that use the default group from any IP address outside the cloud. You can modify the rules in a security group to allow access to instances through different ports and protocols. For example, you can modify rules to allow access to instances through SSH, to ping them, or to allow UDP traffic – for example, for a DNS server running on an instance. You specify the following parameters for rules: Source of traffic. Enable traffic to instances from either IP addresses inside the cloud from other group members or from all IP addresses. Protocol. Choose TCP for SSH, ICMP for pings, or UDP. Destination port on virtual machine. Defines a port range. To open a single port only, enter the same value twice. ICMP does not support ports: Enter values to define the codes and types of ICMP traffic to be allowed. Rules are automatically enforced as soon as you create or modify them. 注: 已通过测试, 修改默认 secgroup 或自定义 secgroup 都可以完成数据访问测试 帮助 [root@station140 ~(keystone_admin)]# nova help | grep secgroup add-secgroup Add a Security Group to a server. list-secgroup List Security Group(s) of a server. remove-secgroup Remove a Security Group from a server. secgroup-add-group-rule secgroup-add-rule Add a rule to a security group. secgroup-create Create a security group. secgroup-delete Delete a security group. secgroup-delete-group-rule secgroup-delete-rule secgroup-list List security groups for the current tenant. secgroup-list-rules secgroup-update Update a security group. 创建自定义安全组 [root@station140 ~(keystone_admin)]# nova secgroup-create terry "allow ping and ssh" +--------------------------------------+-------+--------------------+ | Id | Name | Description | +--------------------------------------+-------+--------------------+ | 6966a8e4-0980-40ad-a409-baac65b60287 | terry | allow ping and ssh | +--------------------------------------+-------+--------------------+ 列出当前所有安全组 [root@station140 ~(keystone_admin)]# nova secgroup-list +--------------------------------------+---------+--------------------+ | Id | Name | Description | +--------------------------------------+---------+--------------------+ | 91a191a6-b89e-4f87-99c0-0fb985985978 | default | default | | 6966a8e4-0980-40ad-a409-baac65b60287 | terry | allow ping and ssh | +--------------------------------------+---------+--------------------+ 列出某个组中的安全规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+----------+--------------+ | | | | | default | | | | | | default | +-------------+-----------+---------+----------+--------------+ 增加规则方法 (允许 ping) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry icmp -1 -1 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 增加规则方法 (允许 ssh) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry tcp 22 22 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 增加规则方法 (允许 dns 外部访问) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry udp 53 53 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 列出自定义组规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules terry +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | | udp | 53 | 53 | 0.0.0.0/0 | | | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 尝试修改 default secgroup 列出 default secgroup 规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+----------+--------------+ | | | | | default | | | | | | default | +-------------+-----------+---------+----------+--------------+ 添加规则 (允许 ping) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default icmp -1 -1 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 添加规则 (允许 ssh) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default tcp 22 22 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 添加规则 (允许 dns外部访问) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default udp 53 53 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 列出默认组规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | | | | | default | | icmp | -1 | -1 | 0.0.0.0/0 | | | tcp | 22 | 22 | 0.0.0.0/0 | | | | | | | default | | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 删除某个实例, 使用中的规则 nova remove-secgroup terry_instance1 terry 注: 在虚拟机启动后, 无法在增加其他规则 

优秀的个人博客,低调大师

openstack 命令行管理十五 - 浮动 IP 管理 (备忘)

帮助 [root@station140 ~(keystone_admin)]# nova help | grep float add-floating-ip Add a floating IP address to a server. floating-ip-bulk-create Bulk create floating ips by range. floating-ip-bulk-delete Bulk delete floating ips by range. floating-ip-bulk-list List all floating ips. floating-ip-create Allocate a floating IP for the current tenant. floating-ip-delete De-allocate a floating IP. floating-ip-list List floating ips for this tenant. floating-ip-pool-list List all floating ip pools. remove-floating-ip Remove a floating IP address from a server. 生成 浮动 IP [root@station140 ~(keystone_admin)]# nova floating-ip-create pub1 +----------------+-------------+----------+------+ | Ip | Instance Id | Fixed Ip | Pool | +----------------+-------------+----------+------+ | 192.168.48.143 | None | None | pub1 | +----------------+-------------+----------+------+ 分配 [root@station140 ~(network_admin)]# nova add-floating-ip terry_instance1 192.168.48.143 查询浮动 IP 分配情况 [root@station140 ~(keystone_admin)]# nova floating-ip-list +----------------+--------------------------------------+-----------+------+ | Ip | Instance Id | Fixed Ip | Pool | +----------------+--------------------------------------+-----------+------+ | 192.168.48.143 | 93d0c9c1-b38b-4fe3-9ae3-400f43276f60 | 10.0.0.50 | pub1 | +----------------+--------------------------------------+-----------+------+ 移除浮动 IP [root@station140 ~(keystone_admin)]# nova floating-ip-delete 192.168.48.143 

优秀的个人博客,低调大师

openstack 命令行管理四 - 资源管理 (备忘)

 配额用于对每个 tenants 进行限制, 如浮动 IP, 内存, CPU, 磁盘, 密钥, 安全规则, 云硬盘等 资源管理帮助 [root@station140 ~(keystone_admin)]# nova help | grep quota quota-class-show List the quotas for a quota class. quota-class-update Update the quotas for a quota class. quota-defaults List the default quotas for a tenant. quota-delete Delete quota for a tenant/user so their quota will quota-show List the quotas for a tenant/user. quota-update Update the quotas for a tenant/user. 可管理资源 fixed-ips 每个 project 可用固定 IP 地址, 必须大于等于实例可用的 IP 地址数量 floating-ips 每个 project 可用的浮动 IP 地址 injected-file-content-bytes 添加的文件最大可包含多少 bytes injected-file-path-bytes 指定的文件目录下最大可包含的文件 bytes injected-files 每个 project 可以包含的文件数量 instances 每个 project 可包含的最多的 instances 数量 key-pairs 每个用户可用的 key-pairs 的数量 metadata-items 每个实例可拥有的 metadata-items 数量 ram 允许每个 project 中的 instances 可用的 ram (MB) 数量 security-group-rules 可用的安全组规则 security-groups 每个 project 的安全组 cores 每个 project 可用的虚拟 CPU 个数 显示 [root@station140 ~(keystone_admin)]# nova quota-defaults +-----------------------------+-------+ | Quota | Limit | +-----------------------------+-------+ | instances | 10 | | cores | 20 | | ram | 51200 | | floating_ips | 10 | | fixed_ips | -1 | | metadata_items | 128 | | injected_files | 5 | | injected_file_content_bytes | 10240 | | injected_file_path_bytes | 255 | | key_pairs | 100 | | security_groups | 10 | | security_group_rules | 20 | +-----------------------------+-------+ 更新方法 [root@station140 ~(keystone_admin)]# nova quota-class-update --instances 20 default [root@station140 ~(keystone_admin)]# nova quota-defaults +-----------------------------+-------+ | Quota | Limit | +-----------------------------+-------+ | instances | 20 | 建议直接通过 horizon 对每个租户进行配额限制, 方便简单, 准确 通过数据库方法对 quota 进行查询会更加准确 表一, 用于查询 内核, 实例, 内存, 安全组资源 mysql> select a.name, b.resource, b.hard_limit from keystone.project a, nova.quotas b where a.enabled=1 and b.deleted=0 and a.id=b.project_id and a.name='admin'; +-------+-----------------------------+------------+ | name | resource | hard_limit | +-------+-----------------------------+------------+ | admin | cores | 500 | | admin | injected_files | 50 | | admin | injected_file_content_bytes | 10240 | | admin | instances | 200 | | admin | metadata_items | 128 | | admin | ram | 1024000 | | admin | security_groups | 10 | | admin | security_group_rules | 20 | +-------+-----------------------------+------------+ 8 rows in set (0.00 sec) 表二, 用于查询云盘大小, 云盘快照, 云盘数量配额 mysql> select a.name, b.resource, b.hard_limit from keystone.project a, cinder.quotas b where a.enabled=1 and b.deleted=0 and a.id=b.project_id and a.name='admin'; +-------+-----------+------------+ | name | resource | hard_limit | +-------+-----------+------------+ | admin | gigabytes | 10000 | | admin | snapshots | 10 | | admin | volumes | 100 | +-------+-----------+------------+ 3 rows in set (0.00 sec) 表三, 用于查询对路由, 网络安全策略, 浮动IP, IP 地址的配额限制 mysql> select a.name, b.resource, b.limit from keystone.project a, neutron.quotas b where a.enabled=1 and a.id=b.tenant_id and a.name='QA'; +------+---------------------+-------+ | name | resource | limit | +------+---------------------+-------+ | QA | router | 1000 | | QA | security_group_rule | 10000 | | QA | subnet | 1000 | | QA | network | 1000 | | QA | security_group | 1000 | | QA | floatingip | 5000 | | QA | port | 8172 | +------+---------------------+-------+ 7 rows in set (0.00 sec)

资源下载

更多资源
腾讯云软件源

腾讯云软件源

为解决软件依赖安装时官方源访问速度慢的问题,腾讯云为一些软件搭建了缓存服务。您可以通过使用腾讯云软件源站来提升依赖包的安装速度。为了方便用户自由搭建服务架构,目前腾讯云软件源站支持公网访问和内网访问。

Nacos

Nacos

Nacos /nɑ:kəʊs/ 是 Dynamic Naming and Configuration Service 的首字母简称,一个易于构建 AI Agent 应用的动态服务发现、配置管理和AI智能体管理平台。Nacos 致力于帮助您发现、配置和管理微服务及AI智能体应用。Nacos 提供了一组简单易用的特性集,帮助您快速实现动态服务发现、服务配置、服务元数据、流量管理。Nacos 帮助您更敏捷和容易地构建、交付和管理微服务平台。

Rocky Linux

Rocky Linux

Rocky Linux(中文名:洛基)是由Gregory Kurtzer于2020年12月发起的企业级Linux发行版,作为CentOS稳定版停止维护后与RHEL(Red Hat Enterprise Linux)完全兼容的开源替代方案,由社区拥有并管理,支持x86_64、aarch64等架构。其通过重新编译RHEL源代码提供长期稳定性,采用模块化包装和SELinux安全架构,默认包含GNOME桌面环境及XFS文件系统,支持十年生命周期更新。

WebStorm

WebStorm

WebStorm 是jetbrains公司旗下一款JavaScript 开发工具。目前已经被广大中国JS开发者誉为“Web前端开发神器”、“最强大的HTML5编辑器”、“最智能的JavaScript IDE”等。与IntelliJ IDEA同源,继承了IntelliJ IDEA强大的JS部分的功能。

用户登录
用户注册