首页 文章 精选 留言 我的

精选列表

搜索[图床管理],共10000篇文章
优秀的个人博客,低调大师

openstack 命令行管理七 - 角色管理 (备忘)

 帮助 [root@station140 ~(keystone_admin)]# keystone help | grep role role-create Create new role. role-delete Delete role. role-get Display role details. role-list List all roles. user-role-add Add role to user user-role-list List roles granted to a user user-role-remove Remove role from user bootstrap Grants a new role to a new user on a new tenant, after 创建方法 [root@station140 ~(keystone_admin)]# keystone role-create --name vgroup +----------+----------------------------------+ | Property | Value | +----------+----------------------------------+ | id | 9ea4fb60241c4a12b3c89630cf3f087a | | name | vgroup | +----------+----------------------------------+ 把用户添加到某个角色中方法 [root@station140 ~(keystone_admin)]# keystone user-role-add --user terry --role vgroup --tenant cloud 显示角色中的用户方法 [root@station140 ~(keystone_admin)]# keystone user-role-list --user terry --tenant cloud <- 必须的参数 +----------------------------------+----------+----------------------------------+----------------------------------+ | id | name | user_id | tenant_id | +----------------------------------+----------+----------------------------------+----------------------------------+ | 9fe2ff9ee4384b1894a90878d3e92bab | _member_ | 8f6478593aa845b3b44eded4aade0f6f | 9467f30b8bba4770a06a687e4584636b | | 9ea4fb60241c4a12b3c89630cf3f087a | vgroup | 8f6478593aa845b3b44eded4aade0f6f | 9467f30b8bba4770a06a687e4584636b | +----------------------------------+----------+----------------------------------+----------------------------------+ 移除角色中的某个用户 [root@station140 ~(keystone_admin)]# keystone user-role-remove --user terry --role vgroup --tenant cloud

优秀的个人博客,低调大师

openstack 命令行管理十 - 密钥管理 (备忘)

 帮助 [root@station140 ~(keystone_admin)]# nova help | grep key flavor-key Set or unset extra_spec for a flavor. keypair-add Create a new key pair for use with instances. keypair-delete Delete keypair given by its name. keypair-list Print a list of keypairs for a user keypair-show Show details about the given keypair. 创建密钥方法 [ 略 ] ssh-keygen 命令 (默认安装时候已经生成密钥) 添加密钥方法 [root@station140 ~(keystone_admin)]# nova keypair-add --pub-key /root/.ssh/id_rsa.pub terrykey 显示密钥方法 [root@station140 ~(keystone_admin)]# nova keypair-list +----------+-------------------------------------------------+ | Name | Fingerprint | +----------+-------------------------------------------------+ | terrykey | 94:b8:9c:2a:31:8c:2c:87:7f:f5:80:24:23:73:f8:e9 | +----------+-------------------------------------------------+ 密钥作用 当 instance 分配了浮动 IP 后, 允许 server 能够直接访问 instance 时候, 才可以利用密钥配对进行访问 假如通过 novnc 进行访问时候, 仍然需要通过 root/password 方法进行访问

优秀的个人博客,低调大师

openstack 命令行管理二 - 镜像管理 (备忘)

帮助 [root@station140 ~(keystone_admin)]# glance help | grep image [--os-image-url OS_IMAGE_URL] [-U OS_IMAGE_URL] [--os-image-api-version OS_IMAGE_API_VERSION] add DEPRECATED! Use image-create instead. delete DEPRECATED! Use image-delete instead. details DEPRECATED! Use image-list instead. image-create Create a new image. image-delete Delete specified image(s). image-download Download a specific image. image-list List images you can access. image-members DEPRECATED! Use member-list instead. image-show Describe a specific image. image-update Update a specific image. index DEPRECATED! Use image-list instead. member-create Share a specific image with a tenant. member-delete Remove a shared image from a tenant. member-images DEPRECATED! Use member-list instead. member-list Describe sharing permissions by image or tenant. show DEPRECATED! Use image-show instead. update DEPRECATED! Use image-update instead. 下载镜像或者自行创建 [ 略 ] 导入镜像方法 [root@localhost tmp]# source /root/keystonerc_admin [root@localhost tmp(keystone_admin)]# glance image-create --name centos5.8_x86_64 --disk-format=qcow2 --container-format=bare --is-public=True --file=/tmp/centos5.8_x86_64_growroot_1.2_20131231.qcow2 +------------------+--------------------------------------+ | Property | Value | +------------------+--------------------------------------+ | checksum | 06de52dfbc2f582115b0c1981c2e3568 | 当前文件 md5 checksum 码 | container_format | bare | | created_at | 2014-02-14T03:33:01 | 导入时间 | deleted | False | | deleted_at | None | | disk_format | qcow2 | 磁盘格式 | id | 2aad80bf-6fbb-4348-bb20-2c07dbf4f687 | 当前磁盘唯一 ID 值 | is_public | True | | min_disk | 0 | | min_ram | 0 | | name | centos5.8_x86_64 | | owner | e3a71a59840c4e88b8740b789c3afb9c | 当前 openstack owner | protected | False | | size | 1151598592 | | status | active | | updated_at | 2014-02-14T03:33:11 | +------------------+--------------------------------------+ 列出当前可用镜像 [root@station140 ~(keystone_admin)]# glance image-list +--------------------------------------+------------------+-------------+------------------+------------+--------+ | ID | Name | Disk Format | Container Format | Size | Status | +--------------------------------------+------------------+-------------+------------------+------------+--------+ | 2aad80bf-6fbb-4348-bb20-2c07dbf4f687 | centos5.8_x86_64 | qcow2 | bare | 1151598592 | active | | 2d6bb00d-002f-4675-ba84-73d90fdc1020 | cirros | qcow2 | bare | 13147648 | active | +--------------------------------------+------------------+-------------+------------------+------------+--------+ [root@station140 ~(keystone_admin)]# glance details ================================================================================ URI: http://192.168.48.140:9292/v1/images/2aad80bf-6fbb-4348-bb20-2c07dbf4f687 Id: 2aad80bf-6fbb-4348-bb20-2c07dbf4f687 Public: Yes Protected: No Name: centos5.8_x86_64 Status: active Size: 1151598592 Disk format: qcow2 Container format: bare Minimum Ram Required (MB): 0 Minimum Disk Required (GB): 0 Owner: e3a71a59840c4e88b8740b789c3afb9c Created at: 2014-02-14T03:33:01 Deleted at: None Updated at: 2014-02-14T03:33:11 ================================================================================ 查询某个镜像详细信息方法 glance image-show 0c47db9c-5f74-4544-8ada-0894c1d2c20c +------------------------+--------------------------------------+ | Property | Value | +------------------------+--------------------------------------+ | Property 'description' | Windows7#_# | | checksum | eaa3a3a6dfe605f6292675018d41afdf | | container_format | bare | | created_at | 2014-09-25T08:33:46 | | deleted | False | | disk_format | qcow2 | | id | 0c47db9c-5f74-4544-8ada-0894c1d2c20c | | is_public | True | | min_disk | 0 | | min_ram | 0 | | name | Win7 | | owner | 3bf7f92c8b1449a8814b1cf15e1d1cda | | protected | False | | size | 3547856896 | | status | active | | updated_at | 2015-06-12T05:24:54 | +------------------------+--------------------------------------+ 删除镜像 [root@station140 ~(keystone_admin)]# nova image-delete cirros 下载镜像 [root@station140~(keystone_admin)]# glance image-download--file /tmp/ centos5.8_x86_64.qcow2 2aad80bf-6fbb-4348-bb20-2c07dbf4f687 

优秀的个人博客,低调大师

openstack 命令行管理十一 - 安全组管理 (备忘)

 参考官方资料 You must modify the rules for the default security group because users cannot access instances that use the default group from any IP address outside the cloud. You can modify the rules in a security group to allow access to instances through different ports and protocols. For example, you can modify rules to allow access to instances through SSH, to ping them, or to allow UDP traffic – for example, for a DNS server running on an instance. You specify the following parameters for rules: Source of traffic. Enable traffic to instances from either IP addresses inside the cloud from other group members or from all IP addresses. Protocol. Choose TCP for SSH, ICMP for pings, or UDP. Destination port on virtual machine. Defines a port range. To open a single port only, enter the same value twice. ICMP does not support ports: Enter values to define the codes and types of ICMP traffic to be allowed. Rules are automatically enforced as soon as you create or modify them. 注: 已通过测试, 修改默认 secgroup 或自定义 secgroup 都可以完成数据访问测试 帮助 [root@station140 ~(keystone_admin)]# nova help | grep secgroup add-secgroup Add a Security Group to a server. list-secgroup List Security Group(s) of a server. remove-secgroup Remove a Security Group from a server. secgroup-add-group-rule secgroup-add-rule Add a rule to a security group. secgroup-create Create a security group. secgroup-delete Delete a security group. secgroup-delete-group-rule secgroup-delete-rule secgroup-list List security groups for the current tenant. secgroup-list-rules secgroup-update Update a security group. 创建自定义安全组 [root@station140 ~(keystone_admin)]# nova secgroup-create terry "allow ping and ssh" +--------------------------------------+-------+--------------------+ | Id | Name | Description | +--------------------------------------+-------+--------------------+ | 6966a8e4-0980-40ad-a409-baac65b60287 | terry | allow ping and ssh | +--------------------------------------+-------+--------------------+ 列出当前所有安全组 [root@station140 ~(keystone_admin)]# nova secgroup-list +--------------------------------------+---------+--------------------+ | Id | Name | Description | +--------------------------------------+---------+--------------------+ | 91a191a6-b89e-4f87-99c0-0fb985985978 | default | default | | 6966a8e4-0980-40ad-a409-baac65b60287 | terry | allow ping and ssh | +--------------------------------------+---------+--------------------+ 列出某个组中的安全规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+----------+--------------+ | | | | | default | | | | | | default | +-------------+-----------+---------+----------+--------------+ 增加规则方法 (允许 ping) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry icmp -1 -1 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 增加规则方法 (允许 ssh) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry tcp 22 22 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 增加规则方法 (允许 dns 外部访问) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule terry udp 53 53 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 列出自定义组规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules terry +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | | udp | 53 | 53 | 0.0.0.0/0 | | | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 尝试修改 default secgroup 列出 default secgroup 规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+----------+--------------+ | | | | | default | | | | | | default | +-------------+-----------+---------+----------+--------------+ 添加规则 (允许 ping) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default icmp -1 -1 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | icmp | -1 | -1 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 添加规则 (允许 ssh) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default tcp 22 22 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | tcp | 22 | 22 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 添加规则 (允许 dns外部访问) [root@station140 ~(keystone_admin)]# nova secgroup-add-rule default udp 53 53 0.0.0.0/0 +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 列出默认组规则 [root@station140 ~(keystone_admin)]# nova secgroup-list-rules default +-------------+-----------+---------+-----------+--------------+ | IP Protocol | From Port | To Port | IP Range | Source Group | +-------------+-----------+---------+-----------+--------------+ | | | | | default | | icmp | -1 | -1 | 0.0.0.0/0 | | | tcp | 22 | 22 | 0.0.0.0/0 | | | | | | | default | | udp | 53 | 53 | 0.0.0.0/0 | | +-------------+-----------+---------+-----------+--------------+ 删除某个实例, 使用中的规则 nova remove-secgroup terry_instance1 terry 注: 在虚拟机启动后, 无法在增加其他规则 

优秀的个人博客,低调大师

openstack 命令行管理十五 - 浮动 IP 管理 (备忘)

帮助 [root@station140 ~(keystone_admin)]# nova help | grep float add-floating-ip Add a floating IP address to a server. floating-ip-bulk-create Bulk create floating ips by range. floating-ip-bulk-delete Bulk delete floating ips by range. floating-ip-bulk-list List all floating ips. floating-ip-create Allocate a floating IP for the current tenant. floating-ip-delete De-allocate a floating IP. floating-ip-list List floating ips for this tenant. floating-ip-pool-list List all floating ip pools. remove-floating-ip Remove a floating IP address from a server. 生成 浮动 IP [root@station140 ~(keystone_admin)]# nova floating-ip-create pub1 +----------------+-------------+----------+------+ | Ip | Instance Id | Fixed Ip | Pool | +----------------+-------------+----------+------+ | 192.168.48.143 | None | None | pub1 | +----------------+-------------+----------+------+ 分配 [root@station140 ~(network_admin)]# nova add-floating-ip terry_instance1 192.168.48.143 查询浮动 IP 分配情况 [root@station140 ~(keystone_admin)]# nova floating-ip-list +----------------+--------------------------------------+-----------+------+ | Ip | Instance Id | Fixed Ip | Pool | +----------------+--------------------------------------+-----------+------+ | 192.168.48.143 | 93d0c9c1-b38b-4fe3-9ae3-400f43276f60 | 10.0.0.50 | pub1 | +----------------+--------------------------------------+-----------+------+ 移除浮动 IP [root@station140 ~(keystone_admin)]# nova floating-ip-delete 192.168.48.143 

优秀的个人博客,低调大师

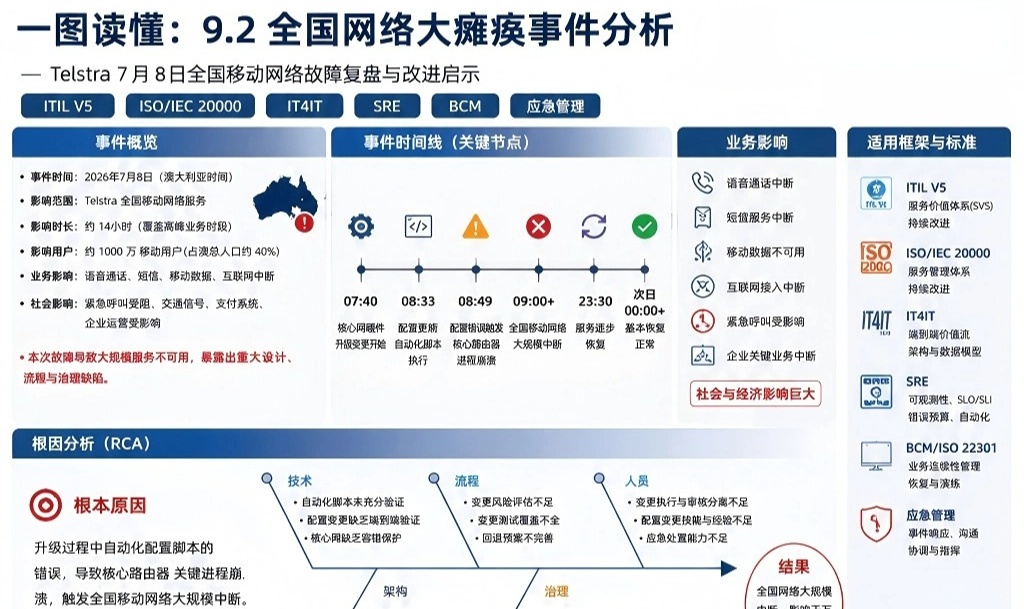
一张图读懂:9.2全国网络大瘫痪事件分析

不是一张GPS卡的故障,而是一套治理体系的失灵:Telstra全国网络大瘫痪深度复盘。——从ITIL V5,ISO20000, IT4IT,SRE与BCM看大型企业为什么会发生“小故障、大事故”?2026年9月2日,澳大利亚最大电信运营商Telstra正式公布了Technology Audit Partners(TAP)针对7月8日全国移动网络大规模故障的外部调查结果。这是一宗非常值得全球CIO、CTO、IT负责人、运维负责人和安全负责人研究的事故。因为它再次证明:大型数字基础设施最大的风险,往往不是我们不知道的风险,而是“我们知道它存在,却没有真正把它当成风险”。一、到底发生了什么?7月8日凌晨,Telstra对其网络授时基础设施进行计划维护。维护过程中,一块GPS授时卡在重新启动后出现异常,将系统日期错误地设置到了2006年。错误时间随后通过Network Time Protocol等授时机制向移动网络传播,并最终造成大范围业务异常。Telstra最初认为事故稍晚开始,但TAP外部调查将事故起点进一步追溯到约凌晨2:50。事故高峰期,Telstra约45%的移动语音和数据会话受到影响,并波及移动通信、数据连接、电子支付、交通以及部分Triple Zero紧急呼叫。Telstra此前披露604次000呼叫未成功连接,调查又识别出另外8次异常呼叫。⚠️从表面看:一次维护 → GPS卡异常 → 时间错误 → 网络故障。💎 但这只是Trigger——触发因素。并不是完整的Root Cause。

资源下载

更多资源
腾讯云软件源

腾讯云软件源

为解决软件依赖安装时官方源访问速度慢的问题,腾讯云为一些软件搭建了缓存服务。您可以通过使用腾讯云软件源站来提升依赖包的安装速度。为了方便用户自由搭建服务架构,目前腾讯云软件源站支持公网访问和内网访问。

Spring

Spring

Spring框架(Spring Framework)是由Rod Johnson于2002年提出的开源Java企业级应用框架,旨在通过使用JavaBean替代传统EJB实现方式降低企业级编程开发的复杂性。该框架基于简单性、可测试性和松耦合性设计理念,提供核心容器、应用上下文、数据访问集成等模块,支持整合Hibernate、Struts等第三方框架,其适用范围不仅限于服务器端开发,绝大多数Java应用均可从中受益。

Rocky Linux

Rocky Linux

Rocky Linux(中文名:洛基)是由Gregory Kurtzer于2020年12月发起的企业级Linux发行版,作为CentOS稳定版停止维护后与RHEL(Red Hat Enterprise Linux)完全兼容的开源替代方案,由社区拥有并管理,支持x86_64、aarch64等架构。其通过重新编译RHEL源代码提供长期稳定性,采用模块化包装和SELinux安全架构,默认包含GNOME桌面环境及XFS文件系统,支持十年生命周期更新。

WebStorm

WebStorm

WebStorm 是jetbrains公司旗下一款JavaScript 开发工具。目前已经被广大中国JS开发者誉为“Web前端开发神器”、“最强大的HTML5编辑器”、“最智能的JavaScript IDE”等。与IntelliJ IDEA同源,继承了IntelliJ IDEA强大的JS部分的功能。

用户登录
用户注册