CentOS下Apache 防盗链配置
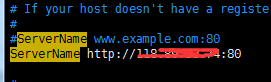
首先在httpd.conf文件中把如下的配置放开,默认是注释掉的 LoadModule rewrite_module modules/mod_rewrite.so 下面是域名 ServerName http://www.xxxx.com 防盗链配置 RewriteEngine On RewriteCond %{HTTP_REFERER} !^http://www.xxxx.com/.*$ [NC] RewriteCond %{HTTP_REFERER} !^http://www.xxxx.com$ [NC] RewriteRule .*\.(gif|png|jpg|swf)$ http://www.xxxx.com/images/error.png [R,NC] RewriteRule .*\.(gif|png|jpg|swf)$ /ALLOW/img/error.jpg [R,NC] RewriteEngine on:开启Rewrite RewriteCond %{HTTP_REFERER} !^http://www.xxxx.com$[NC]:如果网站不是从http://www.xxxx.com域名点开的都会显示error.png RewriteCond中的正则很普通,所以不做说明。RewriteRule中的正则,(.*)代表任意字符,^是开始锚,$是结束锚。