首页 文章 精选 留言 我的

精选列表

搜索[软件合成],共10000篇文章
优秀的个人博客,低调大师

Kdenlive 20.08 发布,视频编辑软件

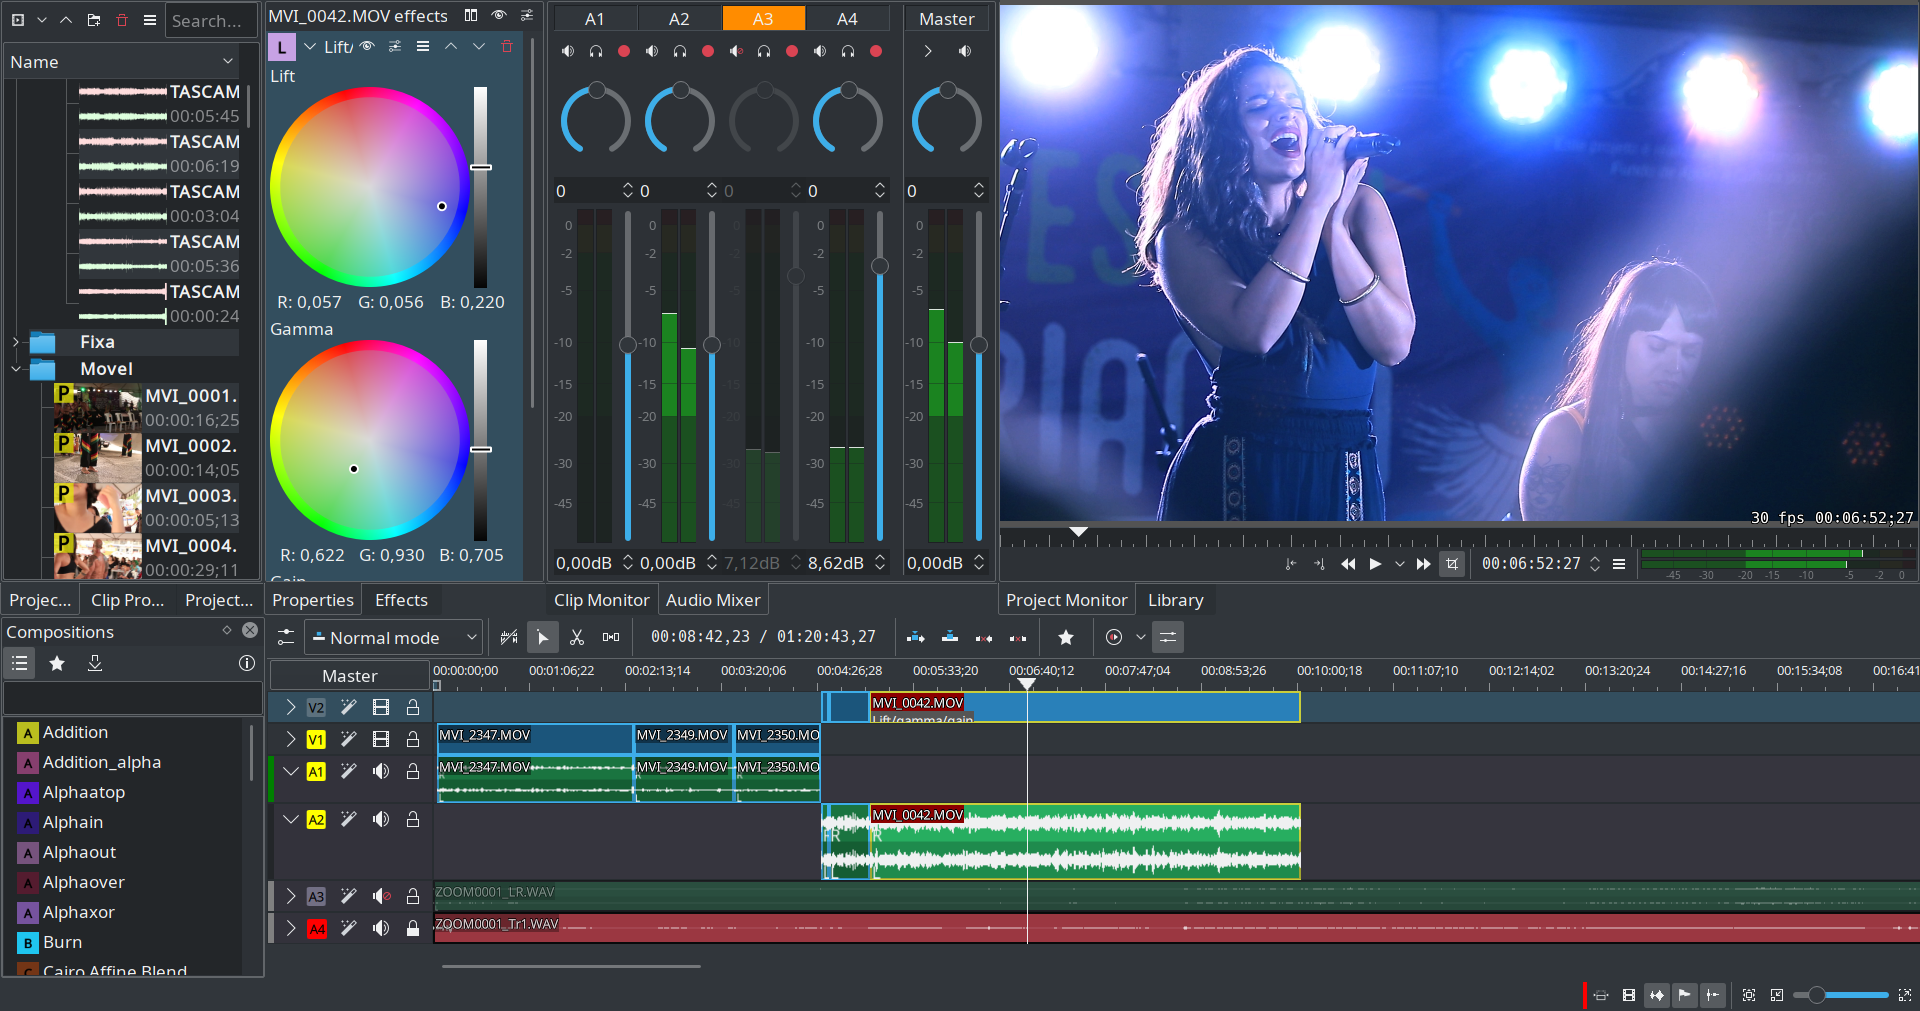
Kdenlive 20.08 现已发布,此版本共收到了 284 个 commits。值得注意的是,使用 20.08 forward 创建的项目不向后兼容,也就是说,用户将无法使用旧版本打开 .kdenlive 项目文件。 更新内容包括有: 新的界面布局 多音频流支持 Clip Monitor 中的缓存数据管理和 Zoombars:新缓存管理界面使用户可以维护和控制缓存和代理文件以及备份数据的大小。同时,用户还可以清除早于指定月份的数据。 效果面板 稳定性和界面改进 详细内容可查看发布说明:https://kdenlive.org/en/2020/08/kdenlive-20-08-is-out/

优秀的个人博客,低调大师

Kdenlive 20.04 发布,视频编辑软件

Kdenlive20.04现已发布,此版本标志着代码重构一年周年。亮点包括由于预览缩放功能而带来的重大速度改进、新评级、对项目箱中的剪辑进行标签排序和过滤以提供出色的记录体验、现在可以在使用速度效果时进行音高转换、Multicam 编辑改进和 OpenTimelineIO支持。 除了所有新功能之外,此版本还修复了 40 个关键的稳定性问题,并对用户体验进行了重大改进。 具体更新内容如下: 预览分辨率:新的预览分辨率通过缩放监视器的视频分辨率来加快编辑体验。 Project Bin:引入过滤器后,日志记录体验变得更好了,用户现在可以对剪辑进行评分和颜色标记。 多机位编辑:新的多机位编辑界面使用户可以通过单击项目监视器在时间轴中选择一个曲目。 音高变化:更改片段速度时的音高补偿功能。 OpentimelineIO导入/导出:为 Pixar 的 OTIO 交换格式增加了导入和导出支持,从而允许与 Final Cut 7 XML、Final Cut Pro X XML 和 Adobe Premiere 互操作性(仅提供完整支持列表)。Kdenlive Windows:即将推出。 运动追踪:运动追踪收到了许多错误修复和新的跟踪算法(CSRT 和 MOSSE)。Kdenlive Windows:即将推出 变焦杆:关键帧的新缩放栏。 界面和可用性 效果组回归 旋转范围:允许在关闭形状之前编辑旋转范围点,Shift +双击以添加新点,双击添加/删除点,双击中心十字以调整大小,仅添加水平/垂直调整大小手柄。 根据时间轴中的类型显示彩色的剪辑。 将剪辑直接拖到时间线。 捕捉:在拖动时按 shift 时禁用捕捉,在使用“间隔器”工具禁用捕捉时按 Shift 键。 在曲目标题中添加菜单可在单个和单独的通道音频缩略图之间切换。 新的启动画面。 渲染配置文件:添加了新的音频配置文件FLA C和ALAC,新的alpha 视频配置文件 VP8、VP9 和 MOV 和GIF图像导出配置文件。 ...... 更多详细信息可查看发布说明:https://kdenlive.org/en/2020/04/kdenlive-20-04-is-out/

优秀的个人博客,低调大师

Kdenlive 19.08.2 发布,视频编辑软件

Kdenlive 19.08.2已经发布,从可用性和用户界面的改进,还有修复bug。内容如下: 修复 Windows 音频屏幕抓取 移除当前项目的本地引用 禁用渲染器上的多轨视图 修复剪辑持续时间在配置文件更改时重置错误的问题 修复编译警告 更新 MSYS 2 构建脚本 修复保留的有效堆栈布局问题 修复使用相对路径打开项目文件时丢失的代理剪辑 更新 AppData 版本 修复混合音轨排序 完整列表见发布说明。

优秀的个人博客,低调大师

VeraCrypt 1.24 发布,开源加密软件

VeraCrypt 1.24 发布,VeraCrypt 是TrueCrypt的分支,于2013年6月发布,项目的主要开发者是来自法国的安全顾问 Mounir Idrassi 。Idrassi 创建 VeraCrypt 分支的动机是在 2012 年他被要求在客户产品中整合 TrueCrypt,他评估了 TrueCrypt代码后发现它存在一些问题,TrueCrypt 的主要弱点是不能防御暴力破解攻击。在加密系统分区时,TrueCrypt 使用 PBKDF2-RIPEMD160 算法进行 1000 次迭代;对于标准容器和非系统分区,TrueCrypt 最多迭代 2000 次。相比之下,VeraCrypt 使用 PBKDF2-RIPEMD160 算法对系统分区迭代 327,661 次,对于标准容器和非系统分区,迭代次数进一步增加到 655,331 次,大幅增加暴力破解难度。结果是,VeraCrypt 打开加密分区的速度略慢,而它的加密格式也不兼容于 TrueCrypt。另一个 TrueCrypt 分支CipherShed项目则努力兼容 TrueCrypt 加密格式。(以上介绍内容来自Solidot) VeraCrypt 增强了用于系统和分区加密的算法的安全性,使其免受暴力破解攻击。VeraCrypt 还解决了TrueCryp t中发现的许多漏洞和安全问题。 以下帖子描述了一些改进和更正:https://veracrypt.codeplex.com/discussions/569777#PostContent_1313325 VeraCrypt on the fly encrypting the system partition : VeraCrypt creating an encrypted volume : 完整改进记录包括: All OSs: Increase password maximum length to 128 bytes in UTF-8 encoding for non-system volumes. Add option to use legacy maximum password length (64) instead of new one for compatibility reasons. Use Hardware RNG based on CPU timing jitter "Jitterentropy" by Stephan Mueller as a good alternative to CPU RDRAND (http://www.chronox.de/jent.html) Speed optimization of XTS mode on 64-bit machine using SSE2 (up to 10% faster). Fix detection of CPU features AVX2/BMI2. Add detection of RDRAND/RDSEED CPU features. Detect Hygon CPU as AMD one. Windows: Implement RAM encryption for keys and passwords using ChaCha12 cipher, t1ha non-cryptographic fast hash and ChaCha20 based CSPRNG. Available only on 64-bit machines. Disabled by default. Can be enabled using option in UI. Less than 10% overhead on modern CPUs. Side effect: Windows Hibernate is not possible if VeraCrypt System Encryption is also being used. Mitigate some memory attacks by making VeraCrypt applications memory inaccessible to non-admin users (based on KeePassXC implementation) New security features: Erase system encryption keys from memory during shutdown/reboot to help mitigate some cold boot attacks Add option when system encryption is used to erase all encryption keys from memory when a new device is connected to the system. Add new driver entry point that can be called by applications to erase encryption keys from memory in case of emergency. MBR Bootloader: dynamically determine boot loader memory segment instead of hardcoded values (proposed by neos6464) MBR Bootloader: workaround for issue affecting creation of hidden OS on some SSD drives. Fix issue related to Windows Update breaking VeraCrypt UEFI bootloader. Several enhancements and fixes for EFI bootloader: Implement timeout mechanism for password input. Set default timeout value to 3 minutes and default timeout action to "shutdown". Implement new actions "shutdown" and "reboot" for EFI DcsProp config file. Enhance Rescue Disk implementation of restoring VeraCrypt loader. Fix ESC on password prompt during Pre-Test not starting Windows. Add menu entry in Rescue Disk that enables starting original Windows loader. Fix issue that was preventing Streebog hash from being selected manually during Pre-Boot authentication. If "VeraCrypt" folder is missing from Rescue Disk, it will boot PC directly from bootloader stored on hard drive This makes it easy to create a bootable disk for VeraCrypt from Rescue Disk just by removing/renaming its "VeraCrypt" folder. Add option (disabled by default) to use CPU RDRAND or RDSEED as an additional entropy source for our random generator when available. Add mount option (both UI and command line) that allows mounting a volume without attaching it to the specified drive letter. Update libzip to version 1.5.2 Do not create uninstall shortcut in startmenu when installing VeraCrypt. (by Sven Strickroth) Enable selection of Quick Format for file containers creation. Separate Quick Format and Dynamic Volume options in the wizard UI. Fix editor of EFI system encryption configuration file not accepting ENTER key to add new lines. Avoid simultaneous calls of favorites mounting, for example if corresponding hotkey is pressed multiple times. Ensure that only one thread at a time can create a secure desktop. Resize some dialogs in Format and Mount Options to fix some text truncation issues with non-English languages. Fix high CPU usage when using favorites and add switch to disable periodic check on devices to reduce CPU load. Minor UI changes. Updates and corrections to translations and documentation. MacOSX: Add check on size of file container during creation to ensure it's smaller than available free disk space. Add CLI switch --no-size-check to disable this check. Linux: Make CLI switch --import-token-keyfiles compatible with Non-Interactive mode. Add check on size of file container during creation to ensure it's smaller than available free disk space. Add CLI switch --no-size-check to disable this check.

资源下载

更多资源
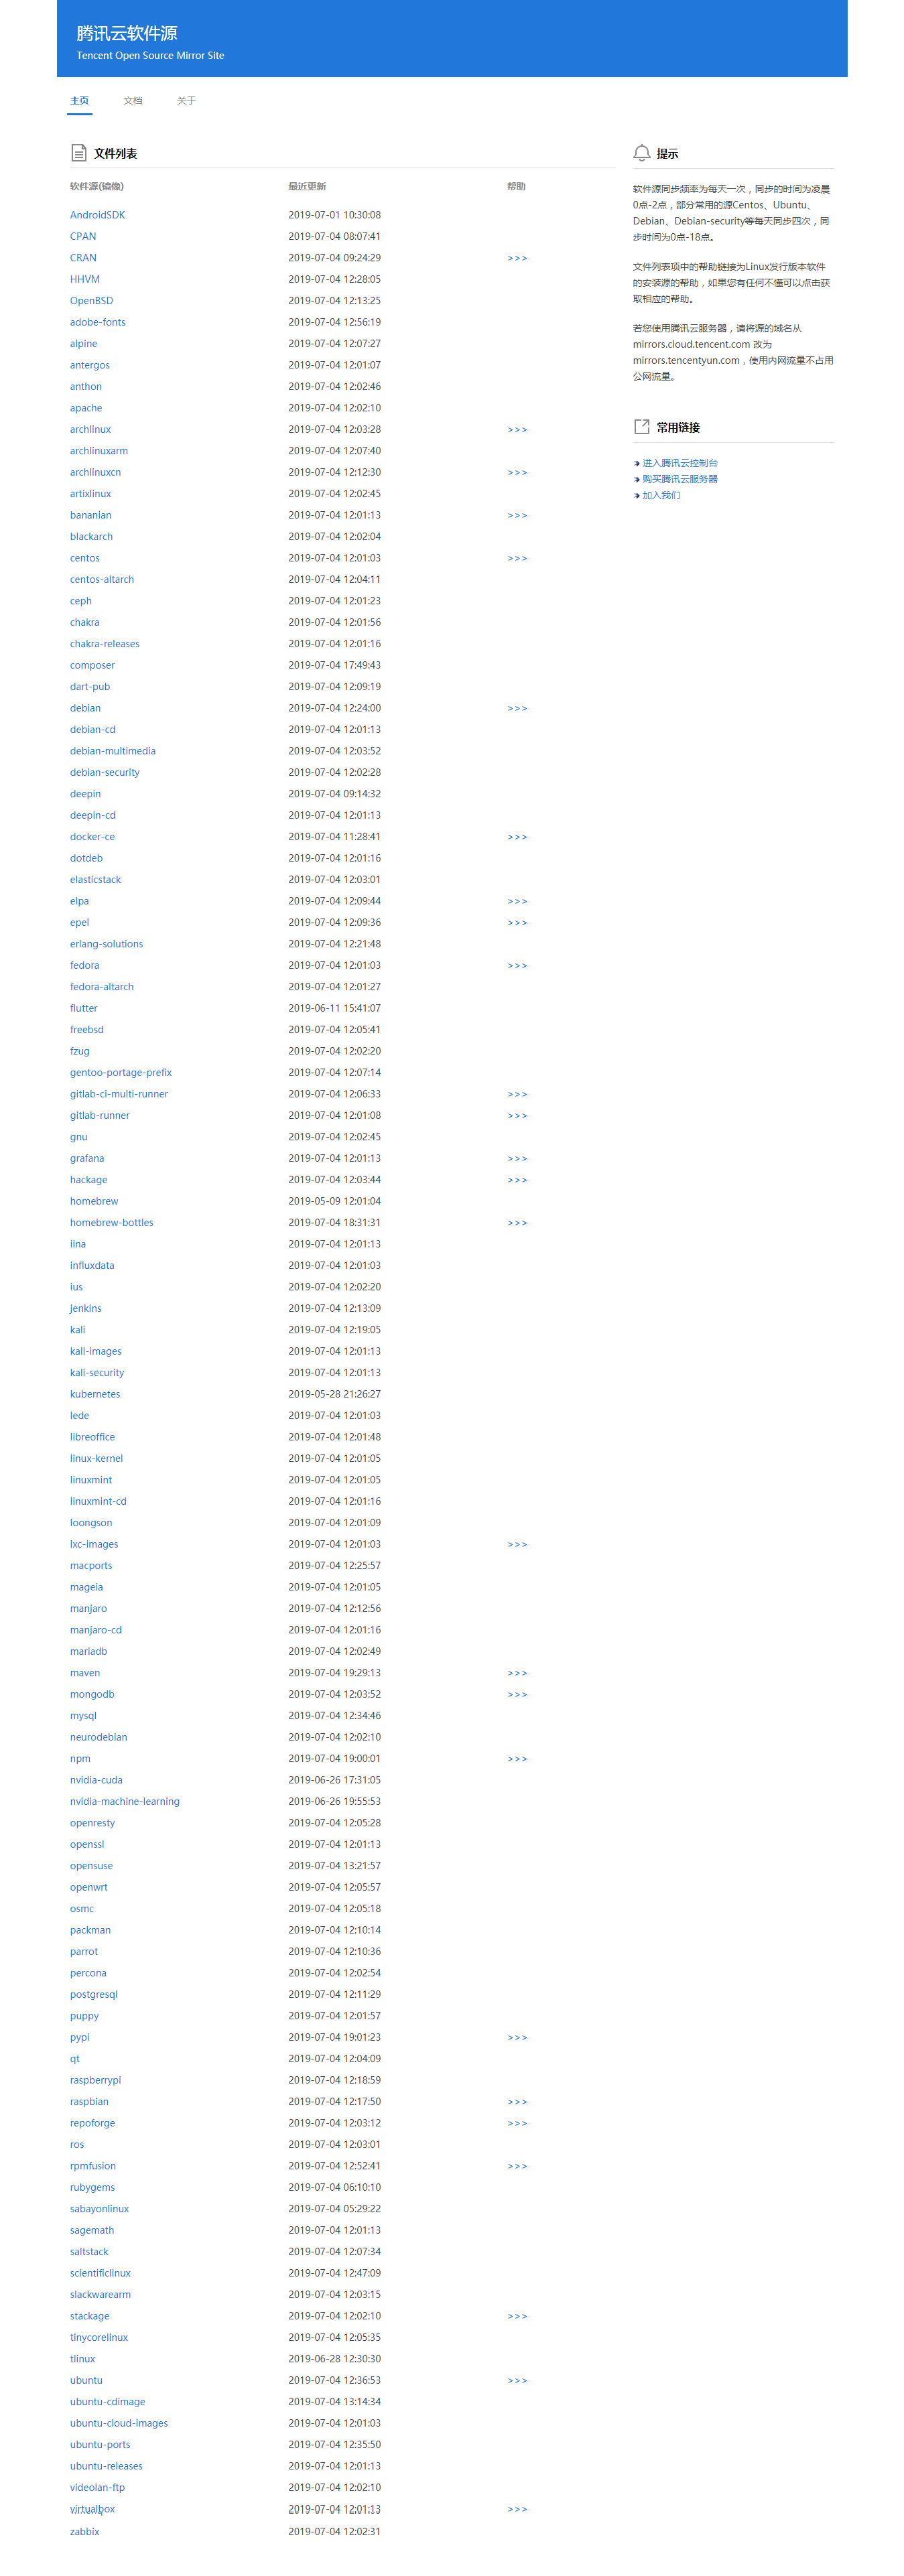
腾讯云软件源

腾讯云软件源

为解决软件依赖安装时官方源访问速度慢的问题,腾讯云为一些软件搭建了缓存服务。您可以通过使用腾讯云软件源站来提升依赖包的安装速度。为了方便用户自由搭建服务架构,目前腾讯云软件源站支持公网访问和内网访问。

Nacos

Nacos

Nacos /nɑ:kəʊs/ 是 Dynamic Naming and Configuration Service 的首字母简称,一个易于构建 AI Agent 应用的动态服务发现、配置管理和AI智能体管理平台。Nacos 致力于帮助您发现、配置和管理微服务及AI智能体应用。Nacos 提供了一组简单易用的特性集,帮助您快速实现动态服务发现、服务配置、服务元数据、流量管理。Nacos 帮助您更敏捷和容易地构建、交付和管理微服务平台。

Spring

Spring

Spring框架(Spring Framework)是由Rod Johnson于2002年提出的开源Java企业级应用框架,旨在通过使用JavaBean替代传统EJB实现方式降低企业级编程开发的复杂性。该框架基于简单性、可测试性和松耦合性设计理念,提供核心容器、应用上下文、数据访问集成等模块,支持整合Hibernate、Struts等第三方框架,其适用范围不仅限于服务器端开发,绝大多数Java应用均可从中受益。

Rocky Linux

Rocky Linux

Rocky Linux(中文名:洛基)是由Gregory Kurtzer于2020年12月发起的企业级Linux发行版,作为CentOS稳定版停止维护后与RHEL(Red Hat Enterprise Linux)完全兼容的开源替代方案,由社区拥有并管理,支持x86_64、aarch64等架构。其通过重新编译RHEL源代码提供长期稳定性,采用模块化包装和SELinux安全架构,默认包含GNOME桌面环境及XFS文件系统,支持十年生命周期更新。

用户登录
用户注册