首页 文章 精选 留言 我的

精选列表

搜索[子系统命令],共10000篇文章
优秀的个人博客,低调大师

ownCloud/Nextcloud OCC命令行工具

列出所有用户 sudo -u apache php /var/www/html/occ user:list 扫描所有用户的所有文件 sudo -u apache php /var/www/html/occ files:scan --all 为用户user1扫描文件: sudo -u apache php /var/www/html/occ files:scan user1 扫描指定用户user1的Photos文件夹 sudo -u apache php /var/www/html/occ files:scan --path="/user1/files/Photos" 格式: files:scan [-p|--path="..."] [-q|--quiet] [-v|vv|vvv --verbose] [--all] [user_id1] ... [user_idN] 参数: user_id #扫描所指定的用户(一个或多个,多个用户ID之间要使用空格分开)的所有文件 选项: --path #限制扫描路径 --all #扫描所有已知用户的所有文件 --quiet #不输出统计信息 --verbose #在扫描过程中显示正在处理的文件和目录 --unscanned #仅扫描以前未扫描过的文件 使用OCC 新建用户 sudo -u apache php /var/www/html/occ user:add test1 Enter password: Confirm password: The user "test1" was created successfully 使用OCC 更改密码 sudo -u apache php /var/www/html/occ user:resetpassword user1 Enter a new password: Confirm the new password: Successfully reset password for user1 用户间文件迁移 sudo -u apache php /var/www/html/occ files:transfer-ownership <来源用户> <目标用户> 进入维护模式 sudo -u apache php /var/www/html/occ maintenance:mode --on sudo -u apache php /var/www/html/occ maintenance:mode --off

优秀的个人博客,低调大师

linux 命令行使用hanlp

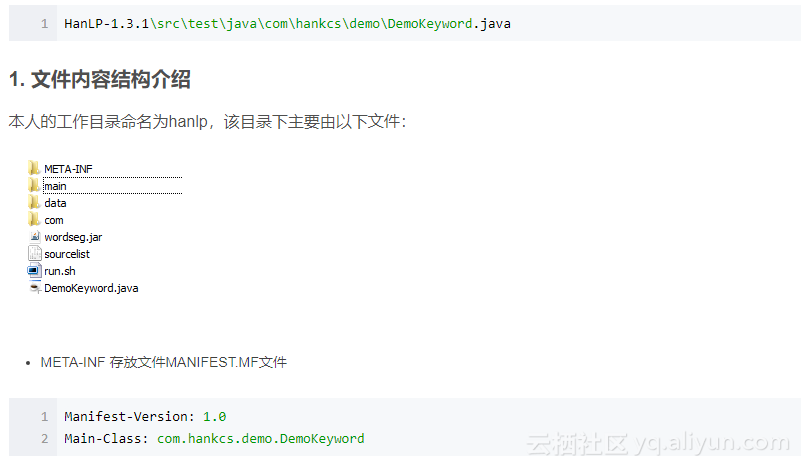
本文主要工作是在linux服务器上使用hanlp, 测试源码主要是hanlp源码中的main 文件夹对应hanlp源码中HanLP-1.3.1srcmain 文件夹。data 文件夹则是hanlp的data文件wordseg.jar 生成的jar文件sourcelist 文件记录了main中所有的java文件,用于对这些文件进行编译run.sh 执行程序的脚本DemoKeyword.java 测试示例文件执行run.sh脚本文件即可得到运行结果: 文章来源于湘笑的博客

优秀的个人博客,低调大师

Docker的常用命令(1)

[root@jiaxin-ceshi logs]# docker help Usage: docker [OPTIONS] COMMAND A self-sufficient runtime for containers Options: --config string Location of client config files (default "/root/.docker") -D, --debug Enable debug mode -H, --host list Daemon socket(s) to connect to -l, --log-level string Set the logging level ("debug"|"info"|"warn"|"error"|"fatal") (default "info") --tls Use TLS; implied by --tlsverify --tlscacert string Trust certs signed only by this CA (default "/root/.docker/ca.pem") --tlscert string Path to TLS certificate file (default "/root/.docker/cert.pem") --tlskey string Path to TLS key file (default "/root/.docker/key.pem") --tlsverify Use TLS and verify the remote -v, --version Print version information and quit Management Commands: config Manage Docker configs container Manage containers image Manage images network Manage networks node Manage Swarm nodes plugin Manage plugins secret Manage Docker secrets service Manage services stack Manage Docker stacks swarm Manage Swarm system Manage Docker trust Manage trust on Docker images volume Manage volumes Commands: attach Attach local standard input, output, and error streams to a running container build Build an image from a Dockerfile commit Create a new image from a container's changes cp Copy files/folders between a container and the local filesystem create Create a new container diff Inspect changes to files or directories on a container's filesystem events Get real time events from the server exec Run a command in a running container export Export a container's filesystem as a tar archive history Show the history of an image images List images import Import the contents from a tarball to create a filesystem image info Display system-wide information inspect Return low-level information on Docker objects kill Kill one or more running containers load Load an image from a tar archive or STDIN login Log in to a Docker registry logout Log out from a Docker registry logs Fetch the logs of a container pause Pause all processes within one or more containers port List port mappings or a specific mapping for the container ps List containers pull Pull an image or a repository from a registry push Push an image or a repository to a registry rename Rename a container restart Restart one or more containers rm Remove one or more containers rmi Remove one or more images run Run a command in a new container save Save one or more images to a tar archive (streamed to STDOUT by default) search Search the Docker Hub for images start Start one or more stopped containers stats Display a live stream of container(s) resource usage statistics stop Stop one or more running containers tag Create a tag TARGET_IMAGE that refers to SOURCE_IMAGE top Display the running processes of a container unpause Unpause all processes within one or more containers update Update configuration of one or more containers version Show the Docker version information wait Block until one or more containers stop, then print their exit codes Run 'docker COMMAND --help' for more information on a command. -V 版本打印版本信息和退出 查看当前运行的容器 [root@jiaxin-ceshi logs]# docker ps 获取镜像docker pull --help docker pull 镜像名称 查看镜像信息 [root@jiaxin-ceshi logs]# docker images 查找景象 [root@jiaxin-ceshi logs]# docker search nginx 下载镜像 [root@jiaxin-ceshi logs]# docker pull nginx

优秀的个人博客,低调大师

Linux中管理用户和组命令

添加用户 useradd 常用选项 -u 设置用户uid -d 家目录路径 -s 登录shell-g 基本组 -G 附加组 例:创建dabao用户 ,设置 uid为1234 useradd -u 1234 dabao 验证dabao用户 id dabao uid=1234(dabao) gid=1234(dabao) 组=1234(dabao) 建立一个用户xiaogege,并且设置禁止登录shell useradd -s /sbin/nologin xiaogege 在用户信息文件/etc/passwd中查看xiaogege用户信息 grep 'xiaogege' /etc/passwd xiaogege:x:1235:1235::/home/xiaogege:/sbin/nologin验证用户 su - xiaogege This account is currently not available. (不能登录) 建立用户xiaojiejie,并且设置附加组为yuema创建附加组 groupadd yuema 创建用户并设置附加组[root@openstack ~]# useradd -G yuema xiaojiejie验证用户[root@openstack ~]# id xiaojiejieuid=1236(xiaojiejie) gid=1237(xiaojiejie) 组=1237(xiaojiejie),1236(yuema)设置登录密码语法格式 : echo '密码' | passwd --stdin 用户名设置dabao用户的密码为123 echo '123' | passwd --stdin dabao 更改用户 dabao 的密码 。passwd:所有的身份验证令牌已经成功更新修改用户属性usermod [选项] 用户名更改dabao的uid为1001 usermod -u1001 dabao [root@openstack ~]# id dabaouid=1001(dabao) gid=1234(dabao) 组=1234(dabao)常用选项 -u 用户id -d 家目录路径 -s 登录shell-g 基本组 -G 附加组删除用户 userdel语法格式 userdle [-r] 用户名 ,加-r的意义在于是否删除用户的家目录,可不加 管理组成员 groupadd 创建一个名为woaiwojia的组 groupadd woaiwojia 验证创建的组 grep 'woaiwojia' /etc/group woaiwojia:x:1238: 把用户加入组 gpasswd gpasswd -a dabao woaiwojia 正在将用户“dabao”加入到“woaiwojia”组中[root@openstack ~]# id dabaouid=1001(dabao) gid=1234(dabao) 组=1234(dabao),1238(woaiwojia) 将dabao从woaiwojia中删除 # gpasswd -d dabao woaiwojia正在将用户“dabao”从“woaiwojia”组中删除[root@openstack ~]# id dabaouid=1001(dabao) gid=1234(dabao) 组=1234(dabao)删除组 groupdel 语法格式 : groupdel 组名 groupdel woaiwojia grep 'woaiwojia' /etc/group

资源下载

更多资源
Mario

Mario

马里奥是站在游戏界顶峰的超人气多面角色。马里奥靠吃蘑菇成长,特征是大鼻子、头戴帽子、身穿背带裤,还留着胡子。与他的双胞胎兄弟路易基一起,长年担任任天堂的招牌角色。

Nacos

Nacos

Nacos /nɑ:kəʊs/ 是 Dynamic Naming and Configuration Service 的首字母简称,一个易于构建 AI Agent 应用的动态服务发现、配置管理和AI智能体管理平台。Nacos 致力于帮助您发现、配置和管理微服务及AI智能体应用。Nacos 提供了一组简单易用的特性集,帮助您快速实现动态服务发现、服务配置、服务元数据、流量管理。Nacos 帮助您更敏捷和容易地构建、交付和管理微服务平台。

Sublime Text

Sublime Text

Sublime Text具有漂亮的用户界面和强大的功能,例如代码缩略图,Python的插件,代码段等。还可自定义键绑定,菜单和工具栏。Sublime Text 的主要功能包括:拼写检查,书签,完整的 Python API , Goto 功能,即时项目切换,多选择,多窗口等等。Sublime Text 是一个跨平台的编辑器,同时支持Windows、Linux、Mac OS X等操作系统。

WebStorm

WebStorm

WebStorm 是jetbrains公司旗下一款JavaScript 开发工具。目前已经被广大中国JS开发者誉为“Web前端开发神器”、“最强大的HTML5编辑器”、“最智能的JavaScript IDE”等。与IntelliJ IDEA同源,继承了IntelliJ IDEA强大的JS部分的功能。

用户登录
用户注册