首页 文章 精选 留言 我的

精选列表

搜索[制谱软件],共10000篇文章
优秀的个人博客,低调大师

VeraCrypt 1.24 发布,开源加密软件

VeraCrypt 1.24 发布,VeraCrypt 是TrueCrypt的分支,于2013年6月发布,项目的主要开发者是来自法国的安全顾问 Mounir Idrassi 。Idrassi 创建 VeraCrypt 分支的动机是在 2012 年他被要求在客户产品中整合 TrueCrypt,他评估了 TrueCrypt代码后发现它存在一些问题,TrueCrypt 的主要弱点是不能防御暴力破解攻击。在加密系统分区时,TrueCrypt 使用 PBKDF2-RIPEMD160 算法进行 1000 次迭代;对于标准容器和非系统分区,TrueCrypt 最多迭代 2000 次。相比之下,VeraCrypt 使用 PBKDF2-RIPEMD160 算法对系统分区迭代 327,661 次,对于标准容器和非系统分区,迭代次数进一步增加到 655,331 次,大幅增加暴力破解难度。结果是,VeraCrypt 打开加密分区的速度略慢,而它的加密格式也不兼容于 TrueCrypt。另一个 TrueCrypt 分支CipherShed项目则努力兼容 TrueCrypt 加密格式。(以上介绍内容来自Solidot) VeraCrypt 增强了用于系统和分区加密的算法的安全性,使其免受暴力破解攻击。VeraCrypt 还解决了TrueCryp t中发现的许多漏洞和安全问题。 以下帖子描述了一些改进和更正:https://veracrypt.codeplex.com/discussions/569777#PostContent_1313325 VeraCrypt on the fly encrypting the system partition : VeraCrypt creating an encrypted volume : 完整改进记录包括: All OSs: Increase password maximum length to 128 bytes in UTF-8 encoding for non-system volumes. Add option to use legacy maximum password length (64) instead of new one for compatibility reasons. Use Hardware RNG based on CPU timing jitter "Jitterentropy" by Stephan Mueller as a good alternative to CPU RDRAND (http://www.chronox.de/jent.html) Speed optimization of XTS mode on 64-bit machine using SSE2 (up to 10% faster). Fix detection of CPU features AVX2/BMI2. Add detection of RDRAND/RDSEED CPU features. Detect Hygon CPU as AMD one. Windows: Implement RAM encryption for keys and passwords using ChaCha12 cipher, t1ha non-cryptographic fast hash and ChaCha20 based CSPRNG. Available only on 64-bit machines. Disabled by default. Can be enabled using option in UI. Less than 10% overhead on modern CPUs. Side effect: Windows Hibernate is not possible if VeraCrypt System Encryption is also being used. Mitigate some memory attacks by making VeraCrypt applications memory inaccessible to non-admin users (based on KeePassXC implementation) New security features: Erase system encryption keys from memory during shutdown/reboot to help mitigate some cold boot attacks Add option when system encryption is used to erase all encryption keys from memory when a new device is connected to the system. Add new driver entry point that can be called by applications to erase encryption keys from memory in case of emergency. MBR Bootloader: dynamically determine boot loader memory segment instead of hardcoded values (proposed by neos6464) MBR Bootloader: workaround for issue affecting creation of hidden OS on some SSD drives. Fix issue related to Windows Update breaking VeraCrypt UEFI bootloader. Several enhancements and fixes for EFI bootloader: Implement timeout mechanism for password input. Set default timeout value to 3 minutes and default timeout action to "shutdown". Implement new actions "shutdown" and "reboot" for EFI DcsProp config file. Enhance Rescue Disk implementation of restoring VeraCrypt loader. Fix ESC on password prompt during Pre-Test not starting Windows. Add menu entry in Rescue Disk that enables starting original Windows loader. Fix issue that was preventing Streebog hash from being selected manually during Pre-Boot authentication. If "VeraCrypt" folder is missing from Rescue Disk, it will boot PC directly from bootloader stored on hard drive This makes it easy to create a bootable disk for VeraCrypt from Rescue Disk just by removing/renaming its "VeraCrypt" folder. Add option (disabled by default) to use CPU RDRAND or RDSEED as an additional entropy source for our random generator when available. Add mount option (both UI and command line) that allows mounting a volume without attaching it to the specified drive letter. Update libzip to version 1.5.2 Do not create uninstall shortcut in startmenu when installing VeraCrypt. (by Sven Strickroth) Enable selection of Quick Format for file containers creation. Separate Quick Format and Dynamic Volume options in the wizard UI. Fix editor of EFI system encryption configuration file not accepting ENTER key to add new lines. Avoid simultaneous calls of favorites mounting, for example if corresponding hotkey is pressed multiple times. Ensure that only one thread at a time can create a secure desktop. Resize some dialogs in Format and Mount Options to fix some text truncation issues with non-English languages. Fix high CPU usage when using favorites and add switch to disable periodic check on devices to reduce CPU load. Minor UI changes. Updates and corrections to translations and documentation. MacOSX: Add check on size of file container during creation to ensure it's smaller than available free disk space. Add CLI switch --no-size-check to disable this check. Linux: Make CLI switch --import-token-keyfiles compatible with Non-Interactive mode. Add check on size of file container during creation to ensure it's smaller than available free disk space. Add CLI switch --no-size-check to disable this check.
优秀的个人博客,低调大师

Aliyun Linux 2 软件更新 - 2019.05.01

1. 添加下列新包: Dragonfly-0.3.0-3.al7: 阿里巴巴开源的基于P2P镜像及文件分发系统,官网:https://d7y.io/ ; tengine-2.3.0-1.al7: 在 Nginx 基础上加入阿里巴巴定制功能的 Web 服务器,官网:http://tengine.taobao.org/ ; luajit-2.0.4-3.1.al7: Just-In-Time Compiler for Lua, Tengine 依赖包; jemalloc-4.0.4-1.1.al7: General-purpose scalable concurrent malloc implementation, Tengine 依赖包; ossfs-1.80.5-1.al7: 支持 Aliyun OSS bucket 挂载到本地文件系统中的

优秀的个人博客,低调大师

Aliyun Linux 2 软件更新 - 2019.04.11

1. 添加下列新包: ebcc-1.0.0-3.1.al7: 基于 BCC 的系统性能分析工具,接下来将推出一系列技术文档,敬请期待; pouch-1.2.0-1.2.al7: 阿里巴巴开源容器 PouchContainer,与 Aliyun Linux 2 集成,开箱即用。 2. 安全更新: libssh2-1.4.3-12.1.al7.2, Upstream: https://access.redhat.com/errata/RHSA-2019:0679 ; thunderbird-60.6.1-1.1.al7, Upstream: https://access.redhat.com/errata/RHSA-2019:0681 ; firefox-60.6.1-1.1.al7, Upstream: https://access.redha

优秀的个人博客,低调大师

用来代替SQUID的软件VARNISH

搭建性能比squid高很多的varnish服务器 [文章作者:jackbillow转载请注明出处:http://www.discuz.net] arnish是一款高性能的开源HTTP加速器,挪威最大的在线报纸 Verdens Gang (http://www.vg.no) 使用3台Varnish代替了原来的12台squid, 性能比以前更好。 varnish的作者Poul-Henning Kamp是FreeBSD的内核开发者之一,他认为现在的计算机比起1975年已经复杂许多。在1975年时,储存媒介只有两 种:内存与硬盘。但现在计算机系统的内存除了主存外,还包括了cpu内的L1、L2,甚至有L3快取。硬盘上也有自己的快取装置,因此squid cache自行处理物件替换的架构不可能得知这些情况而做到最佳化,但操作系统可以得知这些情况,所以这部份的工作应该交给操作系统处理, 这就是 Varnish cache设计架构。 1.下载源码包编译安装: cd /usr/local/src && wgethttp://nchc.dl.sourceforge.net/s ... arnish-1.1.1.tar.gz tar zxvf /usr/local/src/varnish-1.1.1.tar.gz cd /usr/local/src/varnish-1.1.1 ./autogen.sh ./configure --enable-debugging-symbols --enable-developer-warnings --enable-dependency-tracking 注:如果你的gcc版本是4.2.0或更高的版本,可以加上--enable-extra-warnings编译参数,在出错时,得到附加的警告信息。 我这里是用源码包安装的,如果你是redhat或centos可以用rpm包来安装(rpm下载位置:http: //sourceforge.net/project/showfiles.php? group_id=155816&package_id=173643&release_id=533569). 2. 建立cache目录: mkdir -p /cache/varnish/V&& chown -R nobody:nobody /cache 3.编写启动文件: cd /usr/local/varnish/sbin vi start.sh 内容如下: #!/bin/sh # file: go.sh date -u /usr/local/varnish/sbin/varnishd \ -a 10.0.0.129:80 \ -s file,/cache/varnish/V,1024m \ -f /usr/local/varnish/sbin/vg.vcl.default \ -p thread_pool_max=1500 \ -p thread_pools=5 \ -p listen_depth=512 \ -p client_http11=on \ 注:-a 是指定后端服务器的ip或hostname,就象squid做revese proxy时的originserver. 不过这个也可以在vcl里面写。 -f 是指定所用的vcl的文件。 -s 指定cache目录的存储类型,文件位置和大小。 -p 是指定varnish的启动的一些启动参数,可以根据自己的机器配置来优化varnish的性能。 其他参数已经参数的具体含义可以用varnishd --help 来查看。 4.编写vcl: 我的vcl如下: backend default { set backend.host = "127.0.0.1"; set backend.port = "http"; } #我用的是一台机器做测试,使用的backend用的是127.0.0.1:80.如果varnish机器和后台的机器分开的。 写上对应的机器的ip或hostname就可以了。 sub vcl_recv { if (req.request != "GET" && req.request != "HEAD") { pipe; } if (req.http.Expect) { pipe; } if (req.http.Authenticate || req.http.Cookie) { pass; } if (req.request == "GET" && req.url ~ "\.(gif|jpg|swf|css|js)$") { lookup; } lookup; } sub vcl_pipe { pipe; } sub vcl_pass { pass; } sub vcl_hash { hash; } sub vcl_hit { if (!obj.cacheable) { pass; } deliver; } sub vcl_timeout { discard; } sub vcl_discard { discard; } 如果是多个站点在不同的originserver时,可以使用下面配置: backend www { set backend.host = "www.jackbillow.com"; set backend.port = "80"; } backend images { set backend.host = "images.jackbillow.com"; set backend.port = "80"; } sub vcl_recv { if (req.http.host ~ "^(www.)?jackbillow.com$") { set req.http.host = "www.jackbillow.com"; set req.backend = www; } elsif (req.http.host ~ "^images.jackbillow.com$") { set req.backend = images; } else { error 404 "Unknown virtual host"; } 5.启动varnish: /usr/local/varnish/sbin/start.sh Mon Sep3 03:13:19 UTC 2007 file /cache/varnish/V/varnish.tEKXXx (unlinked) size 1073741824 bytes (262144 fs-blocks, 262144 pages) Using old SHMFILE ps waux | grep varnish root 162540.00.0 11200708 ? Ss 10:43 0:00 /usr/local/varnish/sbin/varnishd -a 10.0.0.129:80 -s /varnish/V,1024m -f /usr/local/varnish/sbin/vg.vcl.default -p thread_pool_max 1500 -p thread_pools 5 -p listen_depth 512 -p client_http11 on nobody 162550.00.1 1152552 1808 ? Sl 10:43 0:00 /usr/local/varnish/sbin/varnishd -a 10.0.0.129:80 -s file,/cache/varnish/V,1024m -f /usr/local/varnish/sbin/vg.vcl.default -p thread_pool_max 1500 -p thread_pools 5 -p listen_depth 512 -p client_http11 on 看到上面信息说明varnish正确启动,恭喜你,你已经配置成功了。:) 本文转自 jxwpx 51CTO博客,原文链接:http://blog.51cto.com/jxwpx/216878,如需转载请自行联系原作者

资源下载

更多资源
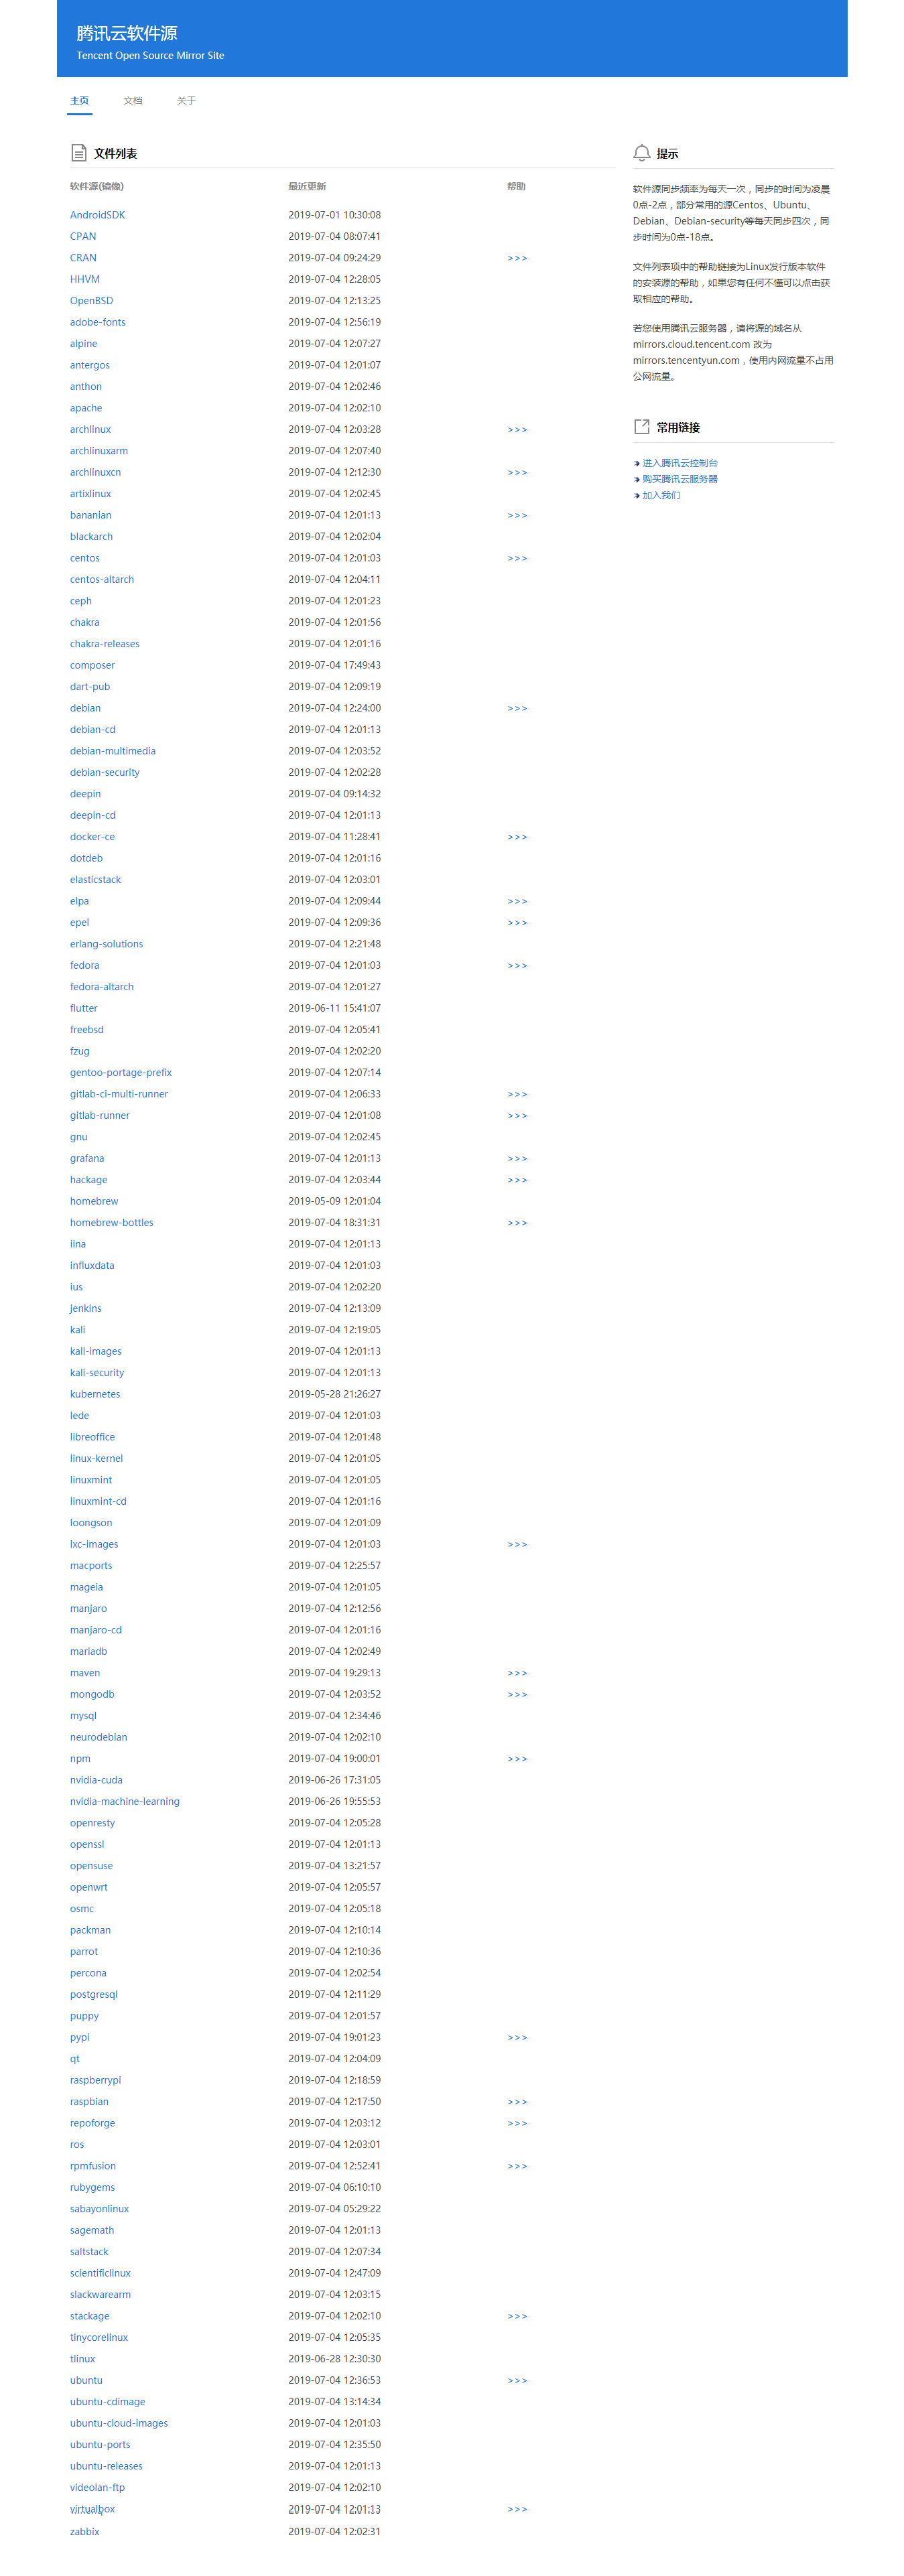
腾讯云软件源

腾讯云软件源

为解决软件依赖安装时官方源访问速度慢的问题,腾讯云为一些软件搭建了缓存服务。您可以通过使用腾讯云软件源站来提升依赖包的安装速度。为了方便用户自由搭建服务架构,目前腾讯云软件源站支持公网访问和内网访问。

Nacos

Nacos

Nacos /nɑ:kəʊs/ 是 Dynamic Naming and Configuration Service 的首字母简称,一个易于构建 AI Agent 应用的动态服务发现、配置管理和AI智能体管理平台。Nacos 致力于帮助您发现、配置和管理微服务及AI智能体应用。Nacos 提供了一组简单易用的特性集,帮助您快速实现动态服务发现、服务配置、服务元数据、流量管理。Nacos 帮助您更敏捷和容易地构建、交付和管理微服务平台。

Sublime Text

Sublime Text

Sublime Text具有漂亮的用户界面和强大的功能,例如代码缩略图,Python的插件,代码段等。还可自定义键绑定,菜单和工具栏。Sublime Text 的主要功能包括:拼写检查,书签,完整的 Python API , Goto 功能,即时项目切换,多选择,多窗口等等。Sublime Text 是一个跨平台的编辑器,同时支持Windows、Linux、Mac OS X等操作系统。

WebStorm

WebStorm

WebStorm 是jetbrains公司旗下一款JavaScript 开发工具。目前已经被广大中国JS开发者誉为“Web前端开发神器”、“最强大的HTML5编辑器”、“最智能的JavaScript IDE”等。与IntelliJ IDEA同源,继承了IntelliJ IDEA强大的JS部分的功能。

用户登录
用户注册