首页 文章 精选 留言 我的

精选列表

搜索[运维监控平台],共10000篇文章
优秀的个人博客,低调大师

马哥运维学习作业(五)

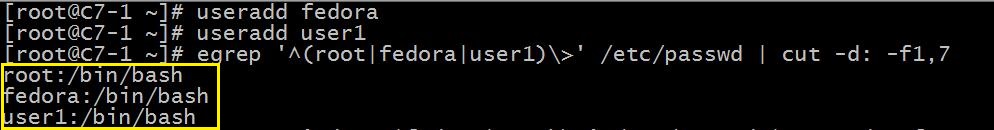
1、显示当前系统上root、fedora或user1用户的默认shell; 1 2 3 4 5 6 [root@C7-1~] #useraddfedora#新建用户fedora [root@C7-1~] #useradduser1#新建用户user1 [root@C7-1~] #egrep'^(root|fedora|user1)\>'/etc/passwd|cut-d:-f1,7#由于(root|fedora|user1)是扩展表达式,所以要使用egrep或grep-E root: /bin/bash fedora: /bin/bash user1: /bin/bash 注:^(root|fedora|user1)\>表示以这三个用户开头的行。cut -d: -f1,7表示以:为分隔符,取第1和第7字段,这二个字段是用户名和shell的。 图示: 2、找出/etc/rc.d/init.d/functions文件中某单词后面跟一组小括号的行,形如:hello(); 1 2 3 4 [root@C7-1~] #egrep-o"^[_[:alpha:]]+\(\)"/etc/rc.d/init.d/functions checkpid() __pids_var_run() ....略 注:根据题目要求,文件中__pids_var_run()也是符合要求的,^[_[:alpha:]]+中,_不能省掉,代表以_或大小写字母开头,+表示前面字符可以出现一次或多次,\(\)是使用转义符来代表小括号() 图示: 3、使用echo命令输出一个绝对路径,使用grep取出其基名; 1 2 3 4 5 6 [root@ cat ~] #echo"/mnt/sdc"|grep-E"[^/]+$"#行尾的字符串[^/]除了/斜线的任意内容,+代表这个/至少出现1次 /mnt/sdc [root@ cat ~] #echo"/mnt/sdc/"|grep-E"[^/]+/?$"#如果sdc后还带一个/,就用/?表示可以出现1次或不出现 /mnt/sdc/ [root@ cat ~] #echo"/mnt/sdc"|grep-E-o"[^/]+/?$"|cut-d"/"-f1#-o只显示匹配的,以/作为分隔符,取第1字段,取出sdc sdc 扩展:取出其路径名 1 2 [root@ cat ~] #echo"/mnt/sdc/test"|grep-o"/.*/"#取出路径名,"/.*/"表示以/开头后面可出现任意长度任意字符,以/结尾,这样就符合路径名的规则。 /mnt/sdc/ 图示: 4、找出ifconfig命令结果中的1-255之间数字; 1 2 3 4 5 6 [root@C7-1~] #ifconfig|grep-E-o"\<([1-9]|[1-9][0-9]|1[0-9]{2}|2[0-4][0-9]|25[0-5])\>" 192 168 2 127 ...略 图示: 5、挑战题:写一个模式,能匹配合理的IP地址; 1 2 3 4 5 6 7 8 [root@ cat ~] #catip#手动写了几个IP地址,有对有错,用下面的条件来筛选 980.168.88.66 192.168.88.255 253.252.251.0 192.168.2.60 255.0.0.690 [root@ cat ~] #grep-E"\<([1-9]|[1-9][0-9]|1[0-9]{2}|2[0-3][0-9])\.([0-9]|[1-9][0-9]|1[0-9]{2}|2[0-4][0-9]|25[0-5])\.([0-9]|[1-9][0-9]|1[0-9]{2}|2[0-4][0-9]|25[0-5])\.([0-9]|[1-9][0-9]|1[0-9]{2}|2[0-4][0-9]|25[0-4])\>"ip 192.168.2.60 6、挑战题:写一个模式,能匹配出所有的邮件地址; 1 2 3 4 5 6 7 8 9 10 11 12 13 14 [root@note1~] #cat/tmp/mail#编写了6个邮箱地址,其中4、5不符合邮箱命名规范 [root@c7-1~] #catmail 342076957@qq.com zhaodongwei@zhaodongwei.cn dongwei_zhao@cmdmedia.cn _dongwei@cmd.cn liupeng@_dfdfd.com zjj.d@baidu.com [root@c7-1~] #egrep-o"[[:alnum:]]+[[:punct:]]*[[:alnum:]]*@[[:alnum:]]+.[[:alnum:]]*.?[[:alnum:]]*"mail 342076957@qq.com zhaodongwei@zhaodongwei.cn dongwei_zhao@cmdmedia.cn dongwei@cmd.cn zjj.d@baidu.com 注:首先,咱们要了解邮箱地址的构成,简单来说,是由:用户名@域名 构成。用户名命名要求:可使用字母、数字、下划线,开头可以使用数字或字母(QQ邮箱就是数字开头)域名命名要求:可使用字母、数字、下划线组成,不能使用特殊字母开头等详细的介绍请看下图:分别是新浪、163邮箱命令介绍。阿里域名的命名介绍 图示: 7、查找/var目录下属主为root,且属组为mail的所有文件或目录; 1 2 3 4 [root@c7-1~] #find/var-userroot-groupmail /var/spool/mail [root@c7-1~] #find/var-userroot-groupmail-ls#-ls是将查找到的文件显示出来 1343212080drwxrwxr-x2rootmail167月3105:06 /var/spool/mail 图示: 8、查找当前系统上没有属主或属组的文件; 1 2 3 4 5 [root@C7-1~] #find/-nouser-o-nogroup-ls#用-nouser-o-nogroup表示没有属 find :‘ /proc/16897/task/16897/fd/6 ’:没有那个文件或目录 find :‘ /proc/16897/task/16897/fdinfo/6 ’:没有那个文件或目录 find :‘ /proc/16897/fd/6 ’:没有那个文件或目录 find :‘ /proc/16897/fdinfo/6 ’:没有那个文件或目录 进一步:查找当前系统上没有属主或属组,且最近3天内曾被访问过的文件或目录; 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 为了方便演示,创建了一个user1的用户,并用user1创建了一个文件,然后删除user1 [user1@C7-1~]$ touch /tmp/b #在user1用户下创建/tmp/b文件 [user1@C7-1~]$ll /tmp/b #查看属主和属组,属于user1 -rw-rw-r--.1user1user109月521:24 /tmp/b [user1@C7-1~]$登出 [root@C7-1~] #登出 [root@C7-1 test ] #登出 [root@C7-1~] #登出 Lastlogin:MonSep521:23:452016 [root@C7-1~] #userdeluser1#退出后,删除user1用户 [root@C7-1~] #iduser1#user1用户已删除 id :user1:nosuchuser [root@C7-1~] #ls-l/tmp/#b文件属主和属组已变为数字 总用量4 -rw-r--r--.1rootroot289月201:2712 -rw-rw-r--.12023202309月521:24b 方法一: [root@note1~] #find/-nouser-a-nogroup-a-atime-3#-atime-3表示3天没有访问过的文件,查找到了b和user1用户下的文件 find :‘ /proc/16901/task/16901/fd/6 ’:没有那个文件或目录 find :‘ /proc/16901/task/16901/fdinfo/6 ’:没有那个文件或目录 find :‘ /proc/16901/fd/6 ’:没有那个文件或目录 find :‘ /proc/16901/fdinfo/6 ’:没有那个文件或目录 /tmp/b /home/tom /home/user1 /home/user1/ .bash_logout /home/user1/ .bash_profile /home/user1/ .bashrc /home/user1/ .bash_history 方法二: [root@C7-1~] #find/\(-nouser-o-nogroup\)-a-atime-3#也可以这样用 find :‘ /proc/16901/task/16901/fd/6 ’:没有那个文件或目录 find :‘ /proc/16901/task/16901/fdinfo/6 ’:没有那个文件或目录 find :‘ /proc/16901/fd/6 ’:没有那个文件或目录 find :‘ /proc/16901/fdinfo/6 ’:没有那个文件或目录 /tmp/b /home/tom /home/user1 /home/user1/ .bash_logout /home/user1/ .bash_profile /home/user1/ .bashrc /home/user1/ .bash_history 图示: 9、查找/etc目录下所有用户都有写权限的文件; 1 2 3 4 5 [root@c7-1~] #find/etc-perm-222-ls#所有用户都有写权限用-perm-222表示 335545640lrwxrwxrwx1rootroot179月500:00 /etc/mtab -> /proc/self/mounts 336897120lrwxrwxrwx1rootroot499月500:01 /etc/pki/tls/certs/ca-bundle .crt-> /etc/pki/ca-trust/extracted/pem/tls-ca-bundle .pem 336897130lrwxrwxrwx1rootroot559月500:01 /etc/pki/tls/certs/ca-bundle .trust.crt-> /etc/pki/ca-trust/extracted/openssl/ca-bundle .trust.crt ...略 10、查找/etc目录下大于1M,且类型为普通文件的所有文件; 1 2 3 [root@c7-1~] #find/etc-size+1M-typef-ls#大于1MB用-size+1M表示 342884416824-r--r--r--1rootroot69848329月500:05 /etc/udev/hwdb .bin 677968023772-rw-r--r--1rootroot385892411月212015 /etc/selinux/targeted/policy/policy .29 11、查找/etc/init.d/目录下,所有用户都有执行权限,且其它用户有写权限的文件; 1 2 [root@c7-1~] #find/etc/init.d-perm-113-ls#用户都有执行,其它用户有写权限用-perm-113表示 336884510lrwxrwxrwx1rootroot119月500:01 /etc/init .d->rc.d /init .d 12、查找/usr目录下不属于root、bin或hadoop的文件; 1 2 3 4 [root@c7-1~] #find/usr-not\(-userroot-o-userbin-o-userhadoop\)-ls#-not放在()外面,对里面的内容,即不也不又不,做条件 674247010drwx------2polkitdroot66月102014 /usr/share/polkit-1/rules .d [root@c7-1~] #find/usr!\(-userroot-o-userbin-o-userhadoop\)-ls#-not和!是同样的意思 674247010drwx------2polkitdroot66月102014 /usr/share/polkit-1/rules .d 13、查找/etc/目录下至少有一类用户没有写权限的文件; 1 2 3 4 [root@c7-1~] #find/etc-not-perm-222-ls#至少一类用户没有写权限用-perm-222表示 3355456112drwxr-xr-x76rootroot81929月504:04 /etc 335545624-rw-r--r--1rootroot4659月500:00 /etc/fstab ....略 14、查找/etc目录下最近一周内其内容被修改过,且不属于root或hadoop的文件; 1 2 3 4 5 6 7 8 9 10 [root@note1~] #ll/etc/test123#默认没有满足条件的文件,所以先在/etc下创建一个test123的文件,查看其属主和属组都是root -rw-r--r--1rootroot0Sep116:00 /etc/test123 [root@note1~] #useraddtest#创建一个test用户,用来把上面文件属主属组都改为test [root@note1~] #chowntest.test/etc/test123#把/etc下的test123改为属主属组root [root@note1~] #ll/etc/test123#已改为root -rw-r--r--1 test test 0Sep116:00 /etc/test123 [root@note1~] #find/etc-mtime-7-a-not-userroot-not-userhadoop#根据题目要求查看,-mtime-7表示7天没修改过 /etc/test123 [root@note1~] #find/etc-mtime-7-not\(-userroot-o-userhadoop\)-ls#-not放外面对里面来做判断,不属于root和hadoop。注意-not放外面要把()里的-a换成-o 3974950-rw-r--r--1 test test 0Sep116:00 /etc/test123 图示: 本文转自cix123 51CTO博客,原文链接:http://blog.51cto.com/zhaodongwei/1845603,如需转载请自行联系原作者

优秀的个人博客,低调大师

Hadoop运维记录系列(二十一)

Zeppelin启用https过程和Hack内核以满足客户需求的记录。 原因是这客户很有意思,该客户中国分公司的人为了验证内网安全性,从国外找了一个***测试小组对Zeppelin和其他产品进行***测试,结果发现Zeppelin主要俩问题,一个是在内网没用https,一个是zeppelin里面可以执行shell命令和python语句。其实这不算大问题,zeppelin本来就是干这个用的。但是***小组不了解zeppelin是做什么的,认为即使在内网里,执行shell命令能查看操作系统的一些文件是大问题,然后发生的事就不说了,不是我们的问题了。 不过既然他们要求整改,我们也只好配合,虽然大家都觉得内网域名加https属于脱了裤子放屁,然后不让zeppelin干他本来应该干的事就更过分了,但鉴于客户是甲方,也只好hack源码了。 于是某个周末用了4个小时完成所有工作。 先记录下zeppelin加https访问,我们有自己的域名证书,所以直接用即可。如果没有域名证书,需要自签发,那么可以看第二部分,双向认证步骤。 https第一部分,已有域名添加jks: opensslpkcs12-export-inxxx.com.crt-inkeyxxx.com.key-outxxx.com.pkcs12 keytool-importkeystore-srckeystorexxx.com.pkcs12-destkeystorexxx.com.jks-srcstoretypepkcs12 https第二部分,自签发证书双向认证添加jks #生成root私钥和证书文件。 opensslgenrsa-outroot.key(pem)2048#Generaterootkeyfile opensslreq-x509-new-keyroot.key(pem)-outroot.crt#Generaterootcertfile #创建客户端私钥和证书以及证书请求文件csr opensslgenrsa-outclient.key(pem)2048#Generateclientkeyfile opensslreq-new-keyclient.key(pem)-outclient.csr#Generateclientcertrequestfile opensslx509-req-inclient.csr-CAroot.crt-CAkeyroot.key(pem)-CAcreateserial-days3650-outclient.crt#Userootcerttogenerateclientcertfile #生成服务器端私钥,证书和证书请求文件csr opensslgenrsa-outserver.key(pem)2048#Generateserverkeyfile,useinZeppelin opensslreq-new-keyserver.key(pem)outserver.csr@Generateservercertrequestfile opensslx509-req-inserver.csr-CAroot.crt-CAkeyroot.key(pem)-CAcreateserial-days3650-outserver.crt#Userootcerttogenerateservercertfile #生成客户端端jks文件 opensslpkcs12-export-inclient.crt-inkeyclient.key(pem)-outclient.pkcs12#Packagetopkcs12format,mustinputapassword,youshouldrememberthepassword keytool-importkeystore-srckeystoreclient.pkcs12-destkeystoreclient.jks-srcstoretypepkcs12#Theclientpasswordyoujustinputatlaststep #生成服务器端jks文件 opensslpkcs12-export-inserver.crt-inkeyserver.key(pem)-outserver.pkcs12@Packagetopkcs12format,mustinputapassword,youshouldrememberthepassword keytool-importkeystore-srckeystoreserver.pkcs12-destkeystoreserver.jks-srcstoretypepkcs12#Theserverpasswordyoujustinputatlaststep 如果是不需要双向认证,只要单向自签发,不创建客户端的各种就可以了。 然后找个地把这些文件放过去,再修改zeppelin配置即可。 mkdir-p/etc/zeppelin/conf/ssl cpserver.crtserver.jks/etc/zeppelin/conf/ssl <property> <name>zeppelin.server.ssl.port</name> <value>8443</value> <description>Serversslport.(usedwhensslpropertyissettotrue)</description> </property> <property> <name>zeppelin.ssl</name> <value>true</value> <description>ShouldSSLbeusedbytheservers?</description> </property> <property> <name>zeppelin.ssl.client.auth</name> <value>false</value> <description>ShouldclientauthenticationbeusedforSSLconnections?</description> </property> <property> <name>zeppelin.ssl.keystore.path</name> <value>/etc/zeppelin/conf/ssl/xxx.com.jks</value> <description>PathtokeystorerelativetoZeppelinconfigurationdirectory</description> </property> <property> <name>zeppelin.ssl.keystore.type</name> <value>JKS</value> <description>Theformatofthegivenkeystore(e.g.JKSorPKCS12)</description> </property> <property> <name>zeppelin.ssl.keystore.password</name> <value>passwordwhichyouinputongeneratingserverjksstep</value> <description>Keystorepassword.CanbeobfuscatedbytheJettyPasswordtool</description> </property> 然后反代那里也加上443的ssl证书以及443转8443的upstream即可。 然后是hack zeppelin源码加入关键字限制,这个确实找了一小会zeppelin发送执行源码给interpreter的地方,zeppelin架构比较清晰,但是代码挺复杂的,用到了很多小花活儿。比如thrift,interpreter脚本里建立nc监听。然后各个解释器插件用socket跟interpreter脚本通信,前端angular,后端jetty,还用shiro做验证和授权。回头可以单开好几篇说说zeppelin安装,使用和详细配置,做这项目基本把zeppelin摸透了。 找到发送前端编写内容给interpreter的java代码,然后用很生硬的办法限制执行命令。具体那个.java文件的名字我就不说了,有悬念有惊喜。我不写java,只负责读源码找到代码位置,hack的java是同事写的。然后编译,替换jar包,完成。后面改了改配置,后续的***测试顺利通过。 staticHashSet<String[]>blockedCodeString=newHashSet<>(); static{ blockedCodeString.add(newString[]{"import","os"}); blockedCodeString.add(newString[]{"import","sys"}); blockedCodeString.add(newString[]{"import","subprocess"}); blockedCodeString.add(newString[]{"import","pty"}); blockedCodeString.add(newString[]{"import","socket"}); blockedCodeString.add(newString[]{"import","commands"}); blockedCodeString.add(newString[]{"import","paramiko"}); blockedCodeString.add(newString[]{"import","pexpect"}); blockedCodeString.add(newString[]{"import","BaseHTTPServer"}); blockedCodeString.add(newString[]{"import","ConfigParser"}); blockedCodeString.add(newString[]{"import","platform"}); blockedCodeString.add(newString[]{"import","popen2"}); blockedCodeString.add(newString[]{"import","copy"}); blockedCodeString.add(newString[]{"import","SocketServer"}); blockedCodeString.add(newString[]{"import","sysconfig"}); blockedCodeString.add(newString[]{"import","tty"}); blockedCodeString.add(newString[]{"import","xmlrpmlib"}); blockedCodeString.add(newString[]{"etc"}); blockedCodeString.add(newString[]{"boot"}); blockedCodeString.add(newString[]{"dev"}); blockedCodeString.add(newString[]{"lib"}); blockedCodeString.add(newString[]{"lib64"}); blockedCodeString.add(newString[]{"lost+found"}); blockedCodeString.add(newString[]{"mnt"}); blockedCodeString.add(newString[]{"proc"}); blockedCodeString.add(newString[]{"root"}); blockedCodeString.add(newString[]{"sbin"}); blockedCodeString.add(newString[]{"selinux"}); blockedCodeString.add(newString[]{"usr"}); blockedCodeString.add(newString[]{"passwd"}); blockedCodeString.add(newString[]{"useradd"}); blockedCodeString.add(newString[]{"userdel"}); blockedCodeString.add(newString[]{"rm"}); blockedCodeString.add(newString[]{"akka"}); blockedCodeString.add(newString[]{"groupadd"}); blockedCodeString.add(newString[]{"groupdel"}); blockedCodeString.add(newString[]{"mkdir"}); blockedCodeString.add(newString[]{"rmdir"}); blockedCodeString.add(newString[]{"ping"}); blockedCodeString.add(newString[]{"nc"}); blockedCodeString.add(newString[]{"telnet"}); blockedCodeString.add(newString[]{"ftp"}); blockedCodeString.add(newString[]{"scp"}); blockedCodeString.add(newString[]{"ssh"}); blockedCodeString.add(newString[]{"ps"}); blockedCodeString.add(newString[]{"hostname"}); blockedCodeString.add(newString[]{"uname"}); blockedCodeString.add(newString[]{"vim"}); blockedCodeString.add(newString[]{"nano"}); blockedCodeString.add(newString[]{"top"}); blockedCodeString.add(newString[]{"cat"}); blockedCodeString.add(newString[]{"more"}); blockedCodeString.add(newString[]{"less"}); blockedCodeString.add(newString[]{"chkconfig"}); blockedCodeString.add(newString[]{"service"}); blockedCodeString.add(newString[]{"netstat"}); blockedCodeString.add(newString[]{"iptables"}); blockedCodeString.add(newString[]{"ip"}); blockedCodeString.add(newString[]{"route"}); blockedCodeString.add(newString[]{"curl"}); blockedCodeString.add(newString[]{"wget"}); blockedCodeString.add(newString[]{"sysctl"}); blockedCodeString.add(newString[]{"touch"}); blockedCodeString.add(newString[]{"scala.sys.process"}); blockedCodeString.add(newString[]{"0.0.0.0"}); blockedCodeString.add(newString[]{"git"}); blockedCodeString.add(newString[]{"svn"}); blockedCodeString.add(newString[]{"hg"}); blockedCodeString.add(newString[]{"cvs"}); blockedCodeString.add(newString[]{"exec"}); blockedCodeString.add(newString[]{"ln"}); blockedCodeString.add(newString[]{"kill"}); blockedCodeString.add(newString[]{"rsync"}); blockedCodeString.add(newString[]{"lsof"}); blockedCodeString.add(newString[]{"crontab"}); blockedCodeString.add(newString[]{"libtool"}); blockedCodeString.add(newString[]{"automake"}); blockedCodeString.add(newString[]{"autoconf"}); blockedCodeString.add(newString[]{"make"}); blockedCodeString.add(newString[]{"gcc"}); blockedCodeString.add(newString[]{"cc"}); } staticbooleanallMatch(Stringaim,String[]checker){ if(checker==null||checker.length<1){ returnfalse; }else{ //bydefault,treatasmatch,everynotmatchchangeit for(Stringi:checker){ if(!aim.matches(".*\\b"+i+"\\b.*")){ returnfalse; } } returntrue; } } staticStringanyMatch(Stringaim,HashSet<String[]>all)throwsException{ if(aim.contains("FUCKP&G")){ thrownewException("Howdoyouknowthis????"); }else{ for(String[]one:all){ if(allMatch(aim,one)){ StringBuildersb=newStringBuilder(); for(Strings:one){ sb.append(s+""); } returnsb.toString(); } } thrownewException("Noonematch"); } } //......此处是个public类 try{ StringmatchesStrings=anyMatch(st,blockedCodeString); result=newInterpreterResult(Code.ERROR,"Containsdangerouscode:"+matchesStrings); }catch(Exceptionme){//nomatchany scheduler.submit(job); while(!job.isTerminated()){ synchronized(jobListener){ try{ jobListener.wait(1000); }catch(InterruptedExceptione){ logger.info("ExceptioninRemoteInterpreterServerwhileinterpret,jobListener.wait",e); } } } if(job.getStatus()==Status.ERROR){ result=newInterpreterResult(Code.ERROR,Job.getStack(job.getException())); }else{ result=(InterpreterResult)job.getReturn(); //incaseofjobabortinPENDINGstatus,resultcanbenull if(result==null){ result=newInterpreterResult(Code.KEEP_PREVIOUS_RESULT); } } } //......直到该public类结束 因为客户有deadline限制,所以快速定位源码位置的过程还是挺有意思的,比较紧张刺激,在这个以小时计算deadline压力下,什么intelliJ, Eclipse都不好使啊,就grep和vi最好用,从找到到改完,比客户定的deadline提前了好几个小时。
优秀的个人博客,低调大师

Apache运维架构之Apache+PHP

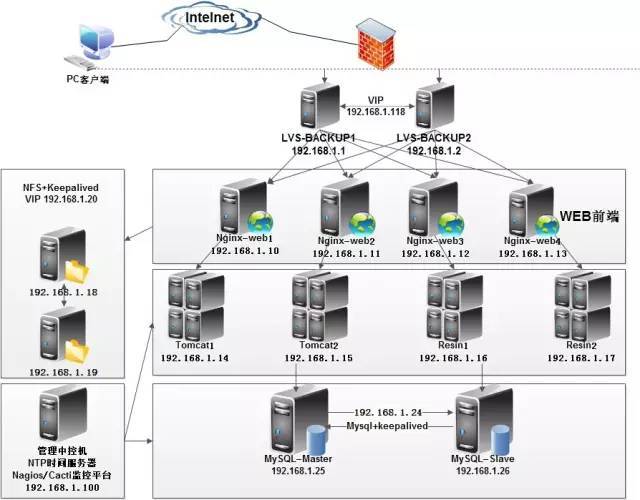
当前互联网主流web服务器说明 1、IIS 微软的web服务器 2、apache 中小web服务器主流,web服务器中的老大哥 3、nginx 新兴的web服务器主流 4、tomcat 中小企业动态服务器,互联网java容器主流 5、resin 大型企业动态服务器,互联网java容器主流 apache的特点及应用场合 特点:功能强大,配置简单,速度快,应用广泛,性能稳定可靠,并可做代理服务器和负载均衡 应用场合: 1、使用apache来运行静态html网页,图片,处理静态小文件能力不及nginx 2、使用apache结合php引擎来运行php程序,lamp由此成为经典组合 3、使用apache结合tomcat及resin运行jsp java等程序,成为中小企业的首选 4、使用apache做代理及负载均衡 本次环境所用到的软件版本如下(操作系统centos6.7) 1、基础环境准备 [root@ansibletools]#tarxfapr-1.4.5.tar.gz [root@ansibletools]#cdapr-1.4.5 [root@ansibleapr-1.4.5]#./configure--prefix=/usr/local/apr [root@ansibleapr-1.4.5]#make&&makeinstall [root@ansibletools]#tarxfapr-util-1.3.12.tar.gz [root@ansibletools]#cdapr-util-1.3.12 [root@ansibleapr-util-1.3.12]#./configure--prefix=/usr/local/apr-util--with-apr=/usr/local/apr/bin/apr-1-config [root@ansibleapr-util-1.3.12]#make&&makeinstall [root@ansiblepcre-8.10]#unzippcre-8.10.zip [root@ansibletools]#cdpcre-8.10 [root@ansiblepcre-8.10]#./configure--prefix=/usr/local/pcre [root@ansiblepcre-8.10]#make&&makeinstall [root@ansibletools]#tarxflibxml2-2.7.6.tar.gz [root@ansibletools]#cdlibxml2-2.7.6 [root@ansiblelibxml2-2.7.6]#vimconfigure将下面那行注释掉 #$RM"$cfgfile" [root@ansiblelibxml2-2.7.6]#./configure--prefix=/usr/local/libxml2--without-zlib [root@ansiblelibxml2-2.7.6]#make&&makeinstall [root@ansibletools]#tarxflibmcrypt-2.5.8.tar.gz [root@ansibletools]#cdlibmcrypt-2.5.8 [root@ansiblelibmcrypt-2.5.8]#./configure--prefix=/usr/local/libmcrypt [root@ansiblelibmcrypt-2.5.8]#make&&makeinstall [root@ansibletools]#tarxfzlib-1.2.5.tar.gz [root@ansibletools]#cdzlib-1.2.5 [root@ansiblezlib-1.2.5]#./configure [root@ansiblezlib-1.2.5]#make&&makeinstall [root@ansibletools]#tarxflibpng-1.4.1.tar.gz [root@ansibletools]#cdlibpng-1.4.1 [root@ansiblelibpng-1.4.1]#./configure--prefix=/usr/local/libpng [root@ansiblelibpng-1.4.1]#make&&makeinstall [root@ansibletools]#mkdir/usr/local/jpeg6 [root@ansibletools]#mkdir/usr/local/jpeg6/bin [root@ansibletools]#mkdir/usr/local/jpeg6/lib [root@ansibletools]#mkdir/usr/local/jpeg6/include [root@ansibletools]#mkdir-p/usr/local/jpeg6/man/man1 [root@ansibletools]#tarxfjpegsrc.v6b.tar.gz [root@ansibletools]#cdjpeg-6b/ [root@ansiblejpeg-6b]#./configure--prefix=/usr/local/jpeg6/--enable-shared--enable-static [root@ansiblejpeg-6b]#make&&make报错 ./libtool--mode=compilegcc-O2-I.-c./jcapimin.c make:./libtool:Commandnotfound make:***[jcapimin.lo]Error127 解决方法 [root@ansibletools]#tarxflibtool-2.2.6a.tar.gz [root@ansibletools]#cdlibtool-2.2.6 [root@ansiblelibtool-2.2.6]#./configure [root@ansiblelibtool-2.2.6]#make&&makeinstall [root@ansiblelibtool-2.2.6]#cd../jpeg-6b/ [root@ansiblejpeg-6b]#cp/usr/share/libtool/config/config.sub. [root@ansiblejpeg-6b]#cp/usr/share/libtool/config/config.guess. [root@ansiblejpeg-6b]#./configure--prefix=/usr/local/jpeg6/--enable-shared--enable-static [root@ansiblejpeg-6b]#make&&make [root@ansibletools]#tarxffreetype-2.3.12.tar.gz [root@ansibletools]#cdfreetype-2.3.12 [root@ansiblefreetype-2.3.12]#./configure--prefix=/usr/local/freetype [root@ansiblefreetype-2.3.12]#make&&makeinstall [root@ansibletools]#tarxfautoconf-2.61.tar.gz [root@ansibletools]#cdautoconf-2.61 [root@ansibleautoconf-2.61]#./configure [root@ansibleautoconf-2.61]#make&&makeinstall [root@ansibletools]#tarxflibgd-2.1.1.tar. libgd-2.1.1.tar.gzlibgd-2.1.1.tar.xz [root@ansibletools]#tarxflibgd-2.1.1.tar.gz [root@ansibletools]#cdlibgd-2.1.1 [root@ansiblelibgd-2.1.1]#./configure\ >--prefix=/usr/local/gd2/\ >--enable-m4_pattern_allow\ >--with-zlib=/usr/local/zlib/\ >--with-jpeg=/usr/local/jpeg6/\ >--with-png=/usr/local/libpng/\ >--with-freetype=/usr/local/freetype/ [root@ansiblelibgd-2.1.1]#make&&makeinstall 2、安装编译apache [root@ansibletools]#useradd-s/sbin/nologin-Mwww [root@ansibletools]#tarxfhttpd-2.4.18.tar.bz2 [root@ansibletools]#cdhttpd-2.4.18 [root@ansiblehttpd-2.4.18]#./configure--prefix=/usr/local/apache2--enable-mods-shared=all--enable-so--enable-proxy-ajp--enable-rewrite--with-apr=/usr/local/apr--with-apr-util=/usr/local/apr-util/--with-pcre=/usr/local/pcre/ [root@ansiblehttpd-2.4.18]#make&&makeinstall 3、安装编译mysql [root@ansiblemysql-5.6.17]#useradd-s/sbin/nologin-Mmysql [root@ansiblemysql-5.6.17]#yuminstallcmake-y [root@ansibletools]#tarxfmysql-5.6.17.tar.gz [root@ansibletools]#cdmysql-5.6.17 [root@ansiblemysql-5.6.17]#cmake\ -DCMAKE_INSTALL_PREFIX=/usr/local/mysql\ -DMYSQL_DATADIR=/usr/local/mysql/data\ -DSYSCONFDIR=/etc\ -DWITH_MYISAM_STORAGE_ENGINE=1\ -DWITH_INNOBASE_STORAGE_ENGINE=1\ -DWITH_MEMORY_STORAGE_ENGINE=1\ -DWITH_READLINE=1\ -DMYSQL_UNIX_ADDR=/var/lib/mysql/mysql.sock\ -DMYSQL_TCP_PORT=3306\ -DENABLED_LOCAL_INFILE=1\ -DWITH_PARTITION_STORAGE_ENGINE=1\ -DEXTRA_CHARSETS=all\ -DDEFAULT_CHARSET=utf8\ -DDEFAULT_COLLATION=utf8_general_ci [root@ansiblemysql-5.6.17]#make&&makeinstall [root@ansiblemysql-5.6.17]#chown-Rmysql.mysql/usr/local/mysql/ [root@ansiblescripts]#pwd /tools/mysql-5.6.17/scripts [root@ansiblescripts]#chmod+xmysql_install_db [root@ansiblescripts]#./mysql_install_db--basedir=/usr/local/mysql--datadir=/usr/local/mysql/data--user=mysql InstallingMySQLsystemtables...2016-08-1913:13:180[Warning]TIMESTAMPwithimplicitDEFAULTvalueisdeprecated.Pleaseuse--explicit_defaults_for_timestampserveroption(seedocumentationformoredetails). 2016-08-1913:13:1864062[Note]InnoDB:Usingatomicstorefcountbufferpoolpages 2016-08-1913:13:1864062[Note]InnoDB:TheInnoDBmemoryheapisdisabled 2016-08-1913:13:1864062[Note]InnoDB:Mutexesandrw_locksuseGCCatomicbuiltins 2016-08-1913:13:1864062[Note]InnoDB:Compressedtablesusezlib1.2.3 2016-08-1913:13:1864062[Note]InnoDB:NotusingCPUcrc32instructions 2016-08-1913:13:1864062[Note]InnoDB:Initializingbufferpool,size=128.0M 2016-08-1913:13:1864062[Note]InnoDB:Completedinitializationofbufferpool 2016-08-1913:13:1864062[Note]InnoDB:Thefirstspecifieddatafile./ibdata1didnotexist:anewdatabasetobecreated! 2016-08-1913:13:1864062[Note]InnoDB:Settingfile./ibdata1sizeto12MB 2016-08-1913:13:1864062[Note]InnoDB:Databasephysicallywritesthefilefull:wait... 2016-08-1913:13:1964062[Note]InnoDB:Settinglogfile./ib_logfile101sizeto48MB 2016-08-1913:13:2164062[Note]InnoDB:Settinglogfile./ib_logfile1sizeto48MB 2016-08-1913:13:2364062[Note]InnoDB:Renaminglogfile./ib_logfile101to./ib_logfile0 2016-08-1913:13:2364062[Warning]InnoDB:Newlogfilescreated,LSN=45781 2016-08-1913:13:2364062[Note]InnoDB:Doublewritebuffernotfound:creatingnew 2016-08-1913:13:2364062[Note]InnoDB:Doublewritebuffercreated 2016-08-1913:13:2364062[Note]InnoDB:128rollbacksegment(s)areactive. 2016-08-1913:13:2364062[Warning]InnoDB:Creatingforeignkeyconstraintsystemtables. 2016-08-1913:13:2364062[Note]InnoDB:Foreignkeyconstraintsystemtablescreated 2016-08-1913:13:2364062[Note]InnoDB:Creatingtablespaceanddatafilesystemtables. 2016-08-1913:13:2364062[Note]InnoDB:Tablespaceanddatafilesystemtablescreated. 2016-08-1913:13:2364062[Note]InnoDB:Waitingforpurgetostart 2016-08-1913:13:2364062[Note]InnoDB:5.6.17started;logsequencenumber0 2016-08-1913:13:2464062[Note]Binlogend 2016-08-1913:13:2464062[Note]InnoDB:FTSoptimizethreadexiting. 2016-08-1913:13:2464062[Note]InnoDB:Startingshutdown... 2016-08-1913:13:2464062[Note]InnoDB:Shutdowncompleted;logsequencenumber1625977 OK Fillinghelptables...2016-08-1913:13:240[Warning]TIMESTAMPwithimplicitDEFAULTvalueisdeprecated.Pleaseuse--explicit_defaults_for_timestampserveroption(seedocumentationformoredetails). 2016-08-1913:13:2464085[Note]InnoDB:Usingatomicstorefcountbufferpoolpages 2016-08-1913:13:2464085[Note]InnoDB:TheInnoDBmemoryheapisdisabled 2016-08-1913:13:2464085[Note]InnoDB:Mutexesandrw_locksuseGCCatomicbuiltins 2016-08-1913:13:2464085[Note]InnoDB:Compressedtablesusezlib1.2.3 2016-08-1913:13:2464085[Note]InnoDB:NotusingCPUcrc32instructions 2016-08-1913:13:2464085[Note]InnoDB:Initializingbufferpool,size=128.0M 2016-08-1913:13:2464085[Note]InnoDB:Completedinitializationofbufferpool 2016-08-1913:13:2464085[Note]InnoDB:HighestsupportedfileformatisBarracuda. 2016-08-1913:13:2464085[Note]InnoDB:128rollbacksegment(s)areactive. 2016-08-1913:13:2564085[Note]InnoDB:Waitingforpurgetostart 2016-08-1913:13:2564085[Note]InnoDB:5.6.17started;logsequencenumber1625977 2016-08-1913:13:2564085[Note]Binlogend 2016-08-1913:13:2564085[Note]InnoDB:FTSoptimizethreadexiting. 2016-08-1913:13:2564085[Note]InnoDB:Startingshutdown... 2016-08-1913:13:2664085[Note]InnoDB:Shutdowncompleted;logsequencenumber1625987 OK Tostartmysqldatboottimeyouhavetocopy support-files/mysql.servertotherightplaceforyoursystem PLEASEREMEMBERTOSETAPASSWORDFORTHEMySQLrootUSER! Todoso,starttheserver,thenissuethefollowingcommands: /usr/local/mysql/bin/mysqladmin-urootpassword'new-password' /usr/local/mysql/bin/mysqladmin-uroot-hansiblepassword'new-password' Alternativelyyoucanrun: /usr/local/mysql/bin/mysql_secure_installation whichwillalsogiveyoutheoptionofremovingthetest databasesandanonymoususercreatedbydefault.Thisis stronglyrecommendedforproductionservers. Seethemanualformoreinstructions. YoucanstarttheMySQLdaemonwith: cd.;/usr/local/mysql/bin/mysqld_safe& YoucantesttheMySQLdaemonwithmysql-test-run.pl cdmysql-test;perlmysql-test-run.pl Pleasereportanyproblemsathttp://bugs.mysql.com/ ThelatestinformationaboutMySQLisavailableonthewebat http://www.mysql.com SupportMySQLbybuyingsupport/licensesathttp://shop.mysql.com Newdefaultconfigfilewascreatedas/usr/local/mysql/my.cnfand willbeusedbydefaultbytheserverwhenyoustartit. Youmayeditthisfiletochangeserversettings 注:在启动MySQL服务时,会按照一定次序搜索my.cnf,先在/etc目录下找,找不到则会搜索"$basedir/my.cnf", 在本例中就是/usr/local/mysql/my.cnf,这是新版MySQL的配置文件的默认位置! [root@ansiblehttpd-2.4.18]#cp/usr/local/mysql/support-files/mysql.server/etc/init.d/mysqld [root@ansiblehttpd-2.4.18]#chmod+x/etc/init.d/mysqld [root@ansiblehttpd-2.4.18]#/etc/init.d/mysqldstart StartingMySQL.......SUCCESS! 4、编译安装php [root@ansiblephp-5.6.18]#yuminstalllibXpm-devel-y [root@ansibletools]#tarxfphp-5.6.18.tar.gz [root@ansibletools]#cdphp-5.6.18 [root@ansiblephp-5.6.18]#./configure\ --prefix=/usr/local/php\ --with-config-file-path=/usr/local/php/etc\ --with-apxs2=/usr/local/apache2/bin/apxs\ --with-mysql=/usr/local/mysql/\ --with-libxml-dir=/usr/local/libxml2/\ --with-png-dir=/usr/local/libpng/\ --with-jpeg-dir=/usr/local/jpeg6/\ --with-freetype-dir=/usr/local/freetype/\ --with-gd=/usr/local/gd2/\ --with-zlib-dir=/usr/local/zlib/\ --with-mcrypt=/usr/local/libmcrypt/\ --with-mysqli=/usr/local/mysql/bin/mysql_config\ --with-xpm-dir=/usr/lib64/\ --enable-soap\ --enable-mbstring=all\ --enable-sockets [root@ansiblephp-5.6.18]#make&&makeinstall 5、apache配置 [root@ansiblephp-5.6.18]#vim/usr/local/apache2/conf/httpd.conf ServerNamelocalhost DirectoryIndexindex.phpindex.html AddType application/x-httpd-php.php.phtml AddTypeapplication/x-httpd-php-source.phps Includeconf/extra/httpd-vhosts.conf LoadModulephp5_modulemodules/libphp5.so Userwww Groupwww [root@ansiblephp-5.6.18]#vim/usr/local/apache2/conf/extra/httpd-vhosts.conf #VirtualHosts <VirtualHost*:80> ServerAdmin1335120568@qq.com DocumentRoot"/usr/local/apache2/htdocs/www" ServerNamewww.martin1.com ServerAliasmartin1.com ErrorLog"logs/www-error_log" CustomLog"logs/www-access_log"common </VirtualHost> <VirtualHost*:80> ServerAdmin1335120568@qq.com DocumentRoot"/usr/local/apache2/htdocs/blog" ServerNameblog.martin1.com ErrorLog"logs/blog-error_log" CustomLog"logs/blog-access_log"common </VirtualHost> [root@ansiblephp-5.6.18]#mkdir-p/usr/local/apache2/htdocs/{www,blog} [root@ansiblephp-5.6.18]#vim/usr/local/apache2/htdocs/www/index.php <?php phpinfo(); ?> [root@ansible php-5.6.18]# /usr/local/apache2/bin/apachectl restart [root@ansible php-5.6.18]# lsof -i :80 COMMAND PID USER FD TYPE DEVICE SIZE/OFF NODE NAME httpd 8307 root 4u IPv6 295815 0t0 TCP *:http (LISTEN) httpd 8309 www 4u IPv6 295815 0t0 TCP *:http (LISTEN) httpd 8310 www 4u IPv6 295815 0t0 TCP *:http (LISTEN) httpd 8312 www 4u IPv6 295815 0t0 TCP *:http (LISTEN) 6、访问测试(如果出现php页面,则说明整合成功) 再简单截图之前编译安装的过程 最后说下如果要在lamp环境下安装编译zabbix 按照如下操作即可 ./configure--prefix=/usr/local/zabbix-server --enable-server --with-mysql--with-net-snmp --with-libcurl --with-libxml2cp -a/home/oldboy/tools/zabbix-3.0.3/frontends/php/* /usr/local/apache2/htdocs/www/

资源下载

更多资源
Mario

Mario

马里奥是站在游戏界顶峰的超人气多面角色。马里奥靠吃蘑菇成长,特征是大鼻子、头戴帽子、身穿背带裤,还留着胡子。与他的双胞胎兄弟路易基一起,长年担任任天堂的招牌角色。

Spring

Spring

Spring框架(Spring Framework)是由Rod Johnson于2002年提出的开源Java企业级应用框架,旨在通过使用JavaBean替代传统EJB实现方式降低企业级编程开发的复杂性。该框架基于简单性、可测试性和松耦合性设计理念,提供核心容器、应用上下文、数据访问集成等模块,支持整合Hibernate、Struts等第三方框架,其适用范围不仅限于服务器端开发,绝大多数Java应用均可从中受益。

Sublime Text

Sublime Text

Sublime Text具有漂亮的用户界面和强大的功能,例如代码缩略图,Python的插件,代码段等。还可自定义键绑定,菜单和工具栏。Sublime Text 的主要功能包括:拼写检查,书签,完整的 Python API , Goto 功能,即时项目切换,多选择,多窗口等等。Sublime Text 是一个跨平台的编辑器,同时支持Windows、Linux、Mac OS X等操作系统。

WebStorm

WebStorm

WebStorm 是jetbrains公司旗下一款JavaScript 开发工具。目前已经被广大中国JS开发者誉为“Web前端开发神器”、“最强大的HTML5编辑器”、“最智能的JavaScript IDE”等。与IntelliJ IDEA同源,继承了IntelliJ IDEA强大的JS部分的功能。

用户登录
用户注册